Evilginx @evilginx
I am the evil bot capturing your MFA tokens. Offensive security reverse-proxy phishing framework capable of bypassing MFA protections, created by @mrgretzky github.com/kgretzky/evilg… Joined May 2018-
Tweets36
-
Followers829
-
Following1
-
Likes40

Black Friday and Cyber Monday deals are out! I review some of them and link to a community GitHub page for you all to get discounts on courses, tools and services! Deals from @_RastaMouse, @_JohnHammond, @offsectraining, @evilginx, @Antisy_Training and a whole lot more. youtu.be/hkJfhM1T5bI

🚨 "Working With Evilginx On-Premises" For projects where OPSEC is critical: keep sensitive data on your server, use cloud only for redirectors. Architecture: Cloudflare → Caddy → Evilginx (on-prem via Tailnet) dan1t0.com/2025/09/24/Wor… @evilginx @mrgretzky #Phishing #OPSEC
The official MFA phishing anthem! 🍪💗🎵

🎵🎧 .lıllılı.ıllı.ılılıılıı.lllııılı. UwU Underground Now Playing: [I Stole Your MFA] 0:44 ———♡———1:52 ◁◁ ▐ ▌ ▷▷ Get Psyopped By New Music, Mammals
🚨 The Black Friday sale is coming! The sale drops at midnight today! (UTC+1) It will be the biggest sale yet! 🤩
Black Friday is on 29th November this year. Just sayin'... 🤫

Merry Christmas everyone! ❄️☃️🎄 Wish you all the best and thank you for a great year! ✨️

Our friend @mrgretzky hooked us up with 12 Evilginx Mastery courses - making it the 12 days of Evilginx Xmas:) Course details: academy.breakdev.org/evilginx-maste… Comment below for a chance to win.
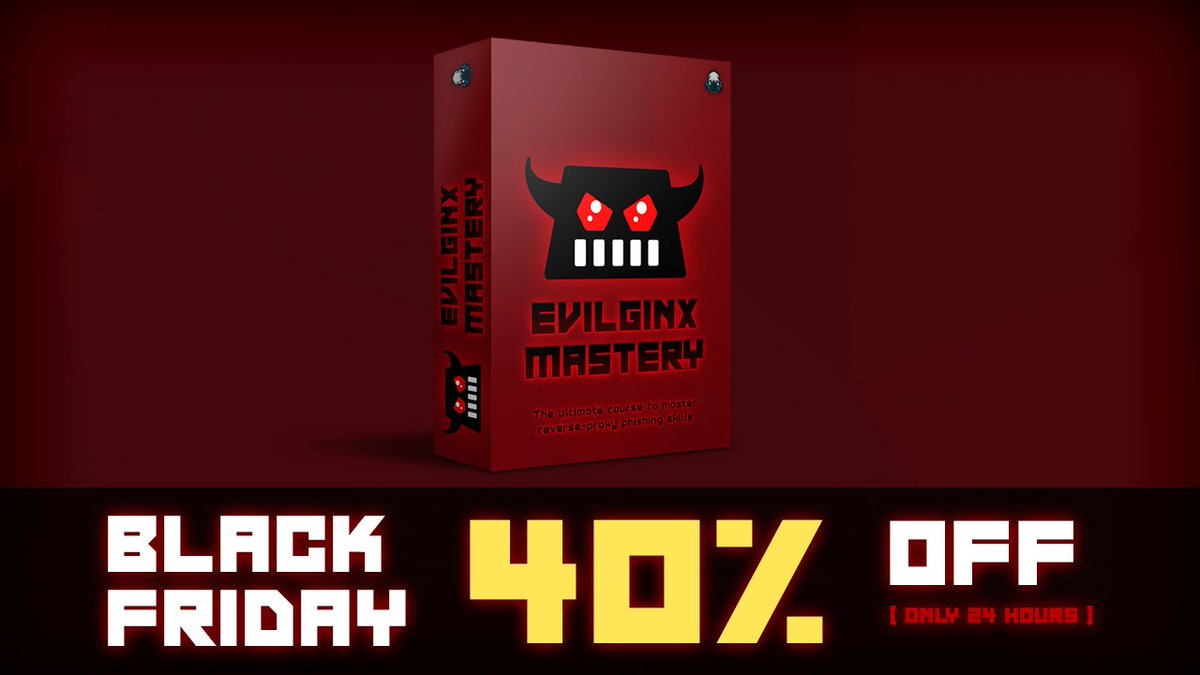
🚨 BLACK FRIDAY Evilginx Mastery -40% SALE 🚨 👑 40% discount (biggest yet!) ⏰ Only 24 hours Code: BLACKFRIDAY40SALE Link: academy.breakdev.org/evilginx-maste… Hurry! It's active only until tomorrow!
🚨 Evilginx Mastery Black Friday SALE is coming... tomorrow! 🔥 It will be the BIGGEST sale so far! 🤩 ⏰ Sale will last only 24 hours.

The @evilginx Mastery course is way too much fun 👀

The purpose of SMS/Push/# matching MFA was to put you past most victims and thus most toolsets. There was a point you were basically immune with legacy protocols turned off in Exchange. Now that stronger methods are normalized, attackers are targeting their weaknesses. Not done.
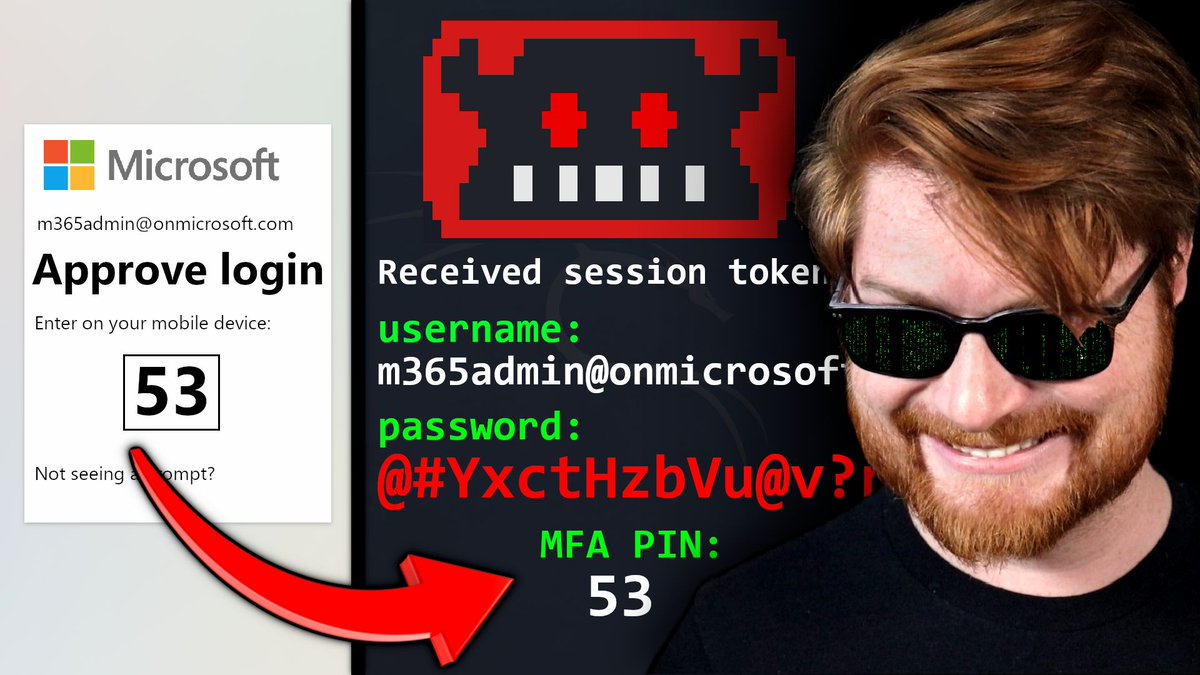
Session hijacking a Microsoft 365 account! Stealing their credentials and bypassing MFA prompt with Evilginx: a reverse-proxy phishing framework! We stage a phishing domain and email pretense, and gain full access to the victim account! youtu.be/sZ22YulJwao
@mwaski88 Round 2 is closed now. Round 3 will open after launch, but you can also reach out privately.
Session hijacking a Microsoft 365 account! Stealing their credentials and bypassing MFA prompt with Evilginx: a reverse-proxy phishing framework! We stage a phishing domain and email pretense, and gain full access to the victim account! youtu.be/sZ22YulJwao
🚨 The big reveal of Evilginx Pro is finally OUT! 🚨 📔From this blog post you will learn what makes the Pro version different from the community one. 🎟️I explain how Evilpuppet secret token extraction works and showcase the core features. Enjoy! 🪝🐟 breakdev.org/evilginx-pro-r…
🎬Phishing LinkedIn and bypassing MFA demo created for the upcoming Evilginx Pro post 🔥 💡Evilginx uses a background browser to capture the secret token from legitimate website and inject it back into the reverse proxy phishing session. P.S. Enjoy that Cyberpunk tune I made 🎵
John Hammond @_JohnHammond
327K Followers 3K Following Cybersecurity Researcher @HuntressLabs Just Hacking Training @JustHackingHQ w/ @ethicalhacker https://t.co/UtsNJiyQtS && https://t.co/narO3sz7y6
mRr3b00t @UK_Daniel_Card
126K Followers 8K Following Chief Artificial Intelligence Cyber Security Scientist Superintelligence-grade security former Helpdesk AI infection status: clean Task Force 29
Kuba Gretzky @mrgretzky
17K Followers 781 Following Creator of Evilginx - Reverse Proxy Phishing Framework for Red Teams: https://t.co/hPg644CTnM
d1rkmtr @d1rkmtr
9K Followers 461 Following
lowercasenumbers @lowernums
0 Followers 53 Following
Mr. Fordham @MrFordham115249
4 Followers 12 Following
Perrault @Perrault1488511
0 Followers 68 Following
TeflonB @teflonbzzzz
9 Followers 71 Following


ketamine @ke8mine
49 Followers 877 Following
pingya lai @linyaping999
1 Followers 93 Following
Darius V @Wall_Sudo
26 Followers 692 Following
Alksx @Alksx0
2 Followers 126 Following


H4CK3R @Oxford_ukwuta
137 Followers 2K Following Ethical hacker|cyber security enthusiast| Python programmer | full time breaker of things, part time maker
Adamu Bola @bola_adamu
106 Followers 536 Following
just D @just858074
0 Followers 6 Following

Dæmon @Kamoli__
310 Followers 158 Following Esq | Vibe-grammer ⚡ | 📚 | CSM | “What’s in it for me — I mean the Alimentum Victus?
Pvstuff @Pvstuffsex
442 Followers 1K Following Packs de todos y para todos🔥 comparte todo es anónimo, también hay aportes de la comunidad
Chan Nik @ChanNik273800
4 Followers 57 Following
Lacrim @LacrimTrading
0 Followers 655 Following
Anomic Xtreme @AnomicXtreme
108 Followers 472 Following
mr.rabbit @rabbit31870_mr
0 Followers 3 Following
Kwashie Addo @adwinmienu
3 Followers 178 Following Most people watch technology happen. I intend to build it.
p1ngp0ng @p1ngp0ng210340
0 Followers 33 Following
Felix @fr1dlix
0 Followers 151 Following

Y41nz @Y4I1nz
11 Followers 285 Following
kzm0523 @kzm2350
7 Followers 419 Following

Владислав О... @z7ppr5t2f8
0 Followers 4 Following
Sui Alchemist @Blessingz69
130 Followers 4K Following Chasing Blockchain dreams, breaking norms and living bold.
Ade 🇳🇬🇳🇬�... @tmadetola
300 Followers 247 Following “The quieter you become, the more you are able to hear” “Only those who will risk going too far, can possibly find out how one can go”
zqtwiter @zqtwiter
5 Followers 427 Following
COCO @Pauloka_y
23 Followers 428 Following

SoporteTImx @SoporteTImx
4 Followers 566 Following
jerbitchiono @Omar_jerbi_
0 Followers 751 Following
mIdHuN @midhung0vind
0 Followers 139 Following
JustCurious @JustCurious7128
1 Followers 396 Following
Anton grimly does his... @flaneur_txt
1K Followers 587 Following it's just myself talking to myself about myself
Brant Hovington @BrantHovington
0 Followers 84 Following
hfz1337 @_hfz1337
2 Followers 43 Following
Ifeanyi @Buziking24
20 Followers 61 Following I am into cryptocurrency, follow me if you wanna make money with cryptocurrency meme coin is life saver, let make money together
Hosein @Hosein635643
4 Followers 868 Following
Stefan Rozek @stefan_roz75472
15 Followers 913 Following
Arsh @arsh_y9
0 Followers 60 Following Tech Enthusiastic | OSINT | Networking | | Cyber Security guy
Unkownd0x @unkownd0x
1 Followers 36 Following
Kuba Gretzky @mrgretzky
17K Followers 781 Following Creator of Evilginx - Reverse Proxy Phishing Framework for Red Teams: https://t.co/hPg644CTnMTrends for United States
You might like