Shellter @shellterproject
AV Evasion Artware || Shellter v7.2 - Executable SHA256: ea07a52eca82b6383c7aa224652e55e0d1701f0779def736977ecadff819049c || Shellter Elite || Dev: @kyREcon shellterproject.com Insainted Ltd Joined September 2015-
Tweets2K
-
Followers5K
-
Following3
-
Likes221
For several months now I've been slowly, but surely, working behind the scenes to dramatically enhance vx-underground. I still don't have a definitive timeline, but I would like to share some stuff coming. 1. All source code will be moved from GitHub to vx-underground. The new vx-underground will have functionality to search through code bases by keywords for research, filter by language type, yada yada yada. 2. Enhanced malware paper searching. It'll be easier to search for stuff now. 3. API access to verified individuals. This is designed for researchers, or organizations, who may want the ability to perform large downloads programmatically. 4. Paid tier. vx-underground will remain free for everyone. However, if you're an organization which makes more than $1,000,000/year you will have to pay for some functionality (malware sample API downloads). I will not charge thousands of dollars, I'm not greedy, but some of you large companies are jerks and need to pay up for scraping the site for AI and samples. API access will be free for individual researchers, small businesses, students, non-profits, and government institutions. Unfortunately, I've learned the hard way large for-profit organizations will not donate. 5. I've heard your complaints for YEARS. We are looking for a HTML-only vx-underground implementation, probably as a subdomain or something. I'm well aware you hardcore nerds hate JavaScript. I will continue investigating this. 6. We're working on our 4th book, Black Mass Volume IV. I have more to announce, but some details are still up in the air. These changes likely won't appear until ... I don't know, bro. I've got a full time job and a family. I'm thinking probably late 2026, early 2027. Thank you to our donors and sponsors that make this possible. I'm not as speedy as I used to be with updates, but I'm still cooking. Cheers -smelly


Many thanks to @nickvourd for bringing our stickers to Defcon 2026. Here's a pick from stickers wall.

You may work on a project for years, but it’s the tiny, inventive touches, the sudden eureka moments, that you remember most. Today had one of those unforgettable ones.
🔥🔥🔥 Shellter Elite v12.3 is now available to download. Enjoy. shellterproject.com/shellter-elite…

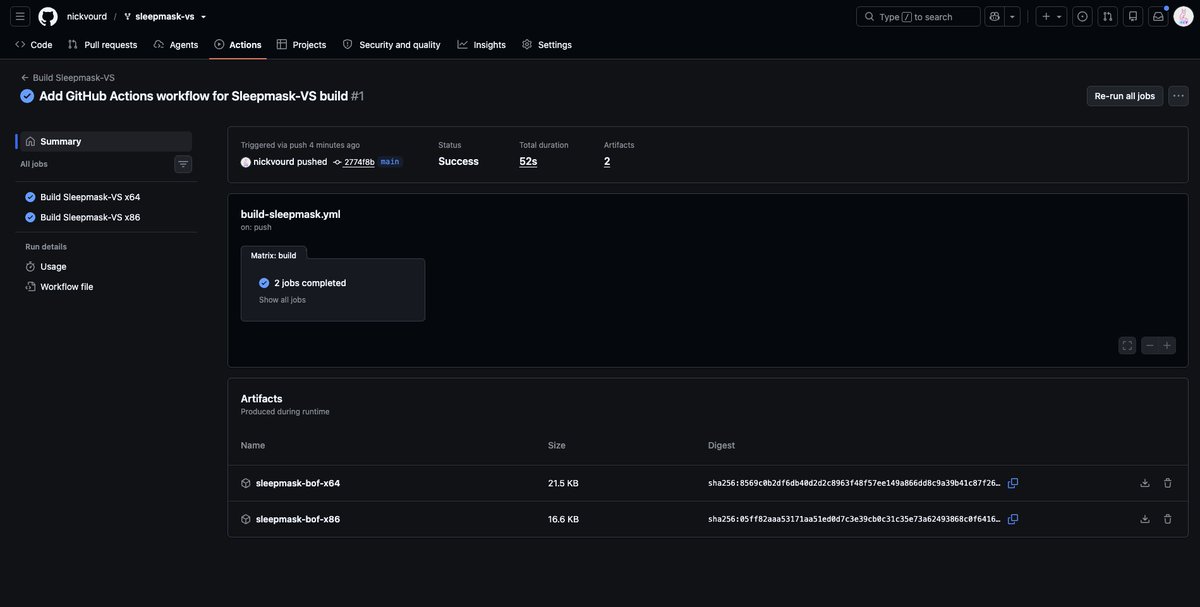
Today I had a fun idea: create a GitHub Actions workflow that fully automates building the sleepmask-vs kit from @_CobaltStrike with a single click. No Visual Studio installation is required. No cross-compilers are needed for ARM/macOS users. Simply trigger the workflow, wait a few moments, and download the compiled artifacts. I've opened a pull request to add this functionality to the official repository: PR: github.com/Cobalt-Strike/… Until it's merged, you can use the workflow from my fork: github.com/nickvourd/slee… #redteam #cobaltstrike


@shellterproject is coming to @defcon… Stay tuned! #redteam


After the recent wave of flags on offensive‑security posts, we weren’t spared, but we did win every appeal. We’re fully reinstated for now, though who knows how long it will last. 💀
@kimmydotzip This happens at the very early stage before the code does anything payload related. Doesn't require code patching or anything else of the usual methods. It suppresses ETW logging for the calling process.
🔥🔥🔥 It’s been a while since our last demo release, but we’re back with a brand-new one. Enjoy! Shellter Elite – Elastic + Defender Evasion – AdaptixC2 Kharon Agent shellterproject.com/shellter-elite…
@nickvourd We are thinking about it.
What do you think guys? Is this legit? 💀

🔥🔥🔥 Shellter Elite v12.2 is now available to download. Enjoy! shellterproject.com/shellter-elite…
🎉🎉🎉 Happy Shellter anniversary! Today marks 12 years since the very first release.

vx-underground @vxunderground
449K Followers 382 Following The largest collection of malware source code, samples, and papers on the internet. Password: infected
Justin Elze @HackingLZ
74K Followers 5K Following CTO @TrustedSec | Former Optiv/SecureWorks/Accuvant Labs/Redspin | Race cars
Adam Chester 🏴�... @_xpn_
39K Followers 554 Following TRACE at @SpecterOps | Blog at https://t.co/tjfTOllCEu
John Hammond @_JohnHammond
327K Followers 3K Following Cybersecurity Researcher @HuntressLabs Just Hacking Training @JustHackingHQ w/ @ethicalhacker https://t.co/UtsNJiyQtS && https://t.co/narO3sz7y6
ippsec @ippsec
125K Followers 372 Following
mRr3b00t @UK_Daniel_Card
126K Followers 8K Following Chief Artificial Intelligence Cyber Security Scientist Superintelligence-grade security former Helpdesk AI infection status: clean Task Force 29
Mike Felch (Stay Read... @ustayready
17K Followers 2K Following Offensive @ TrustedSec | Hacking since Renegade BBS backdoors | Prior CrowdStrike/BHIS | In Christ's grip | Fighter for truth | K1HAQ | RE/VR/ED
an0n @an0n_r0
14K Followers 734 Following CRT(E|O|L) | OSCP | @RingZer0_CTF 1st (for 2yrs) | HackTheBox Top10 | RPISEC MBE | Flare-On completer | GoogleCTF writeup winner | SSD research | Math MSc |🇭🇺
Jake Williams @MalwareJake
151K Followers 2K Following Breaker of software | VP R&D @hunterstrategy | CTI/DFIR | @ians_security faculty | Bookings: jake at malwarejake dot com | GSE #150 | He/him
Stephen Sims @Steph3nSims
26K Followers 876 Following Perpetual Student | SANS Fellow | Musician | Braggart Hater | Gray Hat Hacking | VR | 🏂 | deadcode | https://t.co/4neOSsnCQ8
hacker.house @hackerfantastic
107K Followers 5K Following Co-Founder @MyHackerHouse 💾 | Cybersecurity & Web3 🌐 | Author of Hands-on Hacking (ISBN 9781119561453) 📖 | Offensive Lua 💻 | ✝️
Nikhil @Ox4d5a
19K Followers 2K Following Penetration Tester | i XCHG 0's 1's and do hacks | Red Team Sorcery https://t.co/6LUhkvN2hz | #eJPT | #OSCP | #CRTP | #CRTA | #CESP | #CRTE
Jean @Jean_Maes_1994
12K Followers 1K Following @sansoffensive Certified instructor/SEC565 author/SEC699 co author https://t.co/cp5DerI3g4
JS0N Haddix @Jhaddix
180K Followers 7K Following CEO, CISO, Trainer, Hacker, and Speaker. Cybersecurity + Hacking + AI + Sec Leadership @arcanuminfosec
Clandestine @akaclandestine
65K Followers 5K Following | Security | Osint | Threat Research | Opsec | Threat Intelligence | Infosec | Threat Hunting | Humint |
d1rkmtr @d1rkmtr
9K Followers 461 Following
sn🥶vvcr💥sh @snovvcrash
12K Followers 492 Following Sr. Penetration Tester / Red Team Operator @ptswarm :: Author of the Pentester’s Promiscuous Notebook :: He/him :: Tweets’re my pwn 🐣

EvilMog® @mog.evil.a... @Evil_Mog
18K Followers 2K Following Hacker, Team Hashcat, Bishop of the Church of Wifi, Uber Badge Collector. Views != Employers. Not a Ph.D, Recycled Memes,
Roei Hadashi @roeihadashi
15 Followers 825 Following I break in for a living — and I'm the one they call after someone else did. Head of Red Team & AI Security @ HackersEye
2137 @2137blazeit_
0 Followers 51 Following

Freedom @whatisfreedom25
0 Followers 33 Following
aye @Nurulyasoniq1
0 Followers 460 Following
seNa @thx_sena
75 Followers 666 Following
AYKEO @codywon78906906
46 Followers 1K Following

Shmiffit @B2FIOUD
91 Followers 6K Following Liker. I take each image as it is, regardless. If it appeals to me, I like it. I delete my posts, so catch them while you can. Feel free to DM, I might answer.
Openflaw @Openflaw0
17 Followers 3K Following

perrc @per_rce
0 Followers 157 Following
Ден Куш @idef4ik
5 Followers 314 Following

muchbetter @muchbetterc747
2 Followers 54 Following
M Z @mrzhmud
16 Followers 574 Following
Chirag @Chirag28276456
6 Followers 360 Following A learner, always looking for solutions to crack a probelm.
cr3ghost @cr3ghost
8K Followers 520 Following Curating security, exploit & vulnerability research, tools & free resources | Reverse engineering | Malware | Threat intel | Red/Blue Team | AI | Game Hacking.
bright @Khalid0xf
0 Followers 470 Following

Giorgos Sofronas @gsofron03
2 Followers 15 Following

Kaz @_Kuzushi_
127 Followers 835 Following
CTI Updates @CTI__Updates
2K Followers 3K Following Updates about all things threat intelligence & updates about stuffs going on in the cybersec, ransomware, OSINT, SOCMINT, and hacking communities #threatintel
zer0koan @zer0koan
2 Followers 194 Following
Pete Hewitt - @p373w0... @p373w007
2K Followers 5K Following Child of YBY. Penetration Tester (always learning). Anything I say does NOT necessarily reflect the opinions, policies or tenets of any organization anywhere.
Hacker Stickers @HackerStick3rs
3K Followers 7K Following we're just here to spread neat hacking and cybersecurity related stickers. need high quality vinyl stickers made? DM us.
Rock Stevens @ada95ftw
692 Followers 2K Following Digital security researcher. Former ad model (inadvertantly). PhD in CompSci from @umdcs.
𝚔𝚒𝚖𝚖𝚢.... @kimmydotzip
9K Followers 1K Following Highly Unprofessional | Cyber Treat Actor | Hardcore Wholesome | Failed Man | Poly | Taller than you | TAs say I'm hot | 🥰󠄹󠅞󠄐󠅜󠅟󠅦󠅕󠄐󠅧󠅙󠅤󠅘󠄐󠅑󠅛󠅑󠅞󠅟
Cailloux @Cailloux968499
19 Followers 3K Following
James Morris 👾 @xjamesmorris
1K Followers 2K Following Linux Security @ Microsoft 🐧 Also W7TXT 📡 Supporter of LGBT+ Also: - https://t.co/qC2IlOsvnX - https://t.co/ag0ekLoFOH - https://t.co/f919OsoYZv
yerk @yerkinator21
0 Followers 14 Following
John Smith @JohnSmithhmw8
4 Followers 278 Following
bios @biosh3ll
32 Followers 436 Following
rameinstein @ramkuma07104869
342 Followers 5K Following SecBug Hunter, Ethical Hacker,Quantum Physics research,Chess player,Singer,Music-Brain research, AI-psychologist
Horus-labs @_horus_labs
8 Followers 265 Following
Darren Webb ☠🕷 @spyd3r
1K Followers 8K Following Computational demonologist. The following tweets are classified SECRET GOLD JULY BOOJUM. 101 824 5150
V @0xf4wk3s
427 Followers 1K Following offsec, threat intelligence researcher -. . / -- ..- - .-.. ..- / - ..- .-. -.- ..- -- / -.. .. -.-- . -. . #redteam #OSINT #threatintelligence #ultrAslan
🕴🏻 @ilegalizar
116 Followers 408 Following
nt!RajKit @NtRajkit
24 Followers 422 Following Jellybee the cutting-edge red team C2 and module tradecraft system.
gk98 @98erKAG
55 Followers 3K Following
Bhbth @bhbth
2 Followers 304 Following
0xFF assemblydev(%rip... @assemblydevyt
8 Followers 141 Following My pfp is not mine, I took it from pin, unfortunately I can't find the link, to whoever made it, I'm deeply sorry to not have given credit :(
tdq @edrufc1
7 Followers 349 Following
moncef @mon_cef011
8 Followers 603 Following
c0sm4ky @c0sm4ky
33 Followers 1K Following
Matt Carin @mattcarin41
921 Followers 4K Following Cyber Warfare/OSINT/Blackhat @WarOnTheRocks Contributor. Ukraine/Russia War.
vx-underground @vxunderground
449K Followers 382 Following The largest collection of malware source code, samples, and papers on the internet. Password: infected
The Wider Front 👁�... @WiderFrontHQ
107K Followers 0 Following Independent analysis of wars, military strategy, defence technology & geopolitics. Conflict, context and a wider perspective. Not affiliated with any government
You might like