Ayush Anand @Securityinbits
Detection engineering, threat hunting, malware analysis. One defender bit at a time. newsletter.securityinbits.com Join for free → Joined September 2015-
Tweets722
-
Followers2K
-
Following340
-
Likes1K
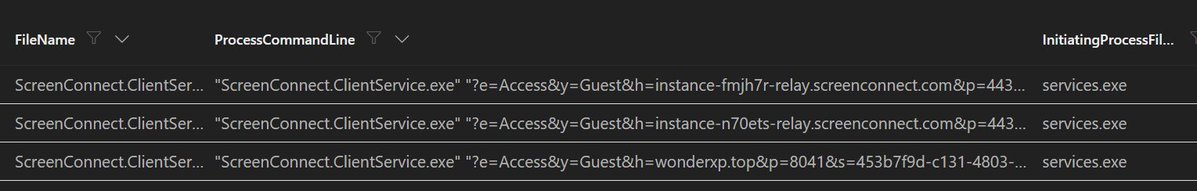
An attacker pointed a signed ScreenConnect client at their own relay. The command line gave it up.
?e=Access&y=Guest&h=
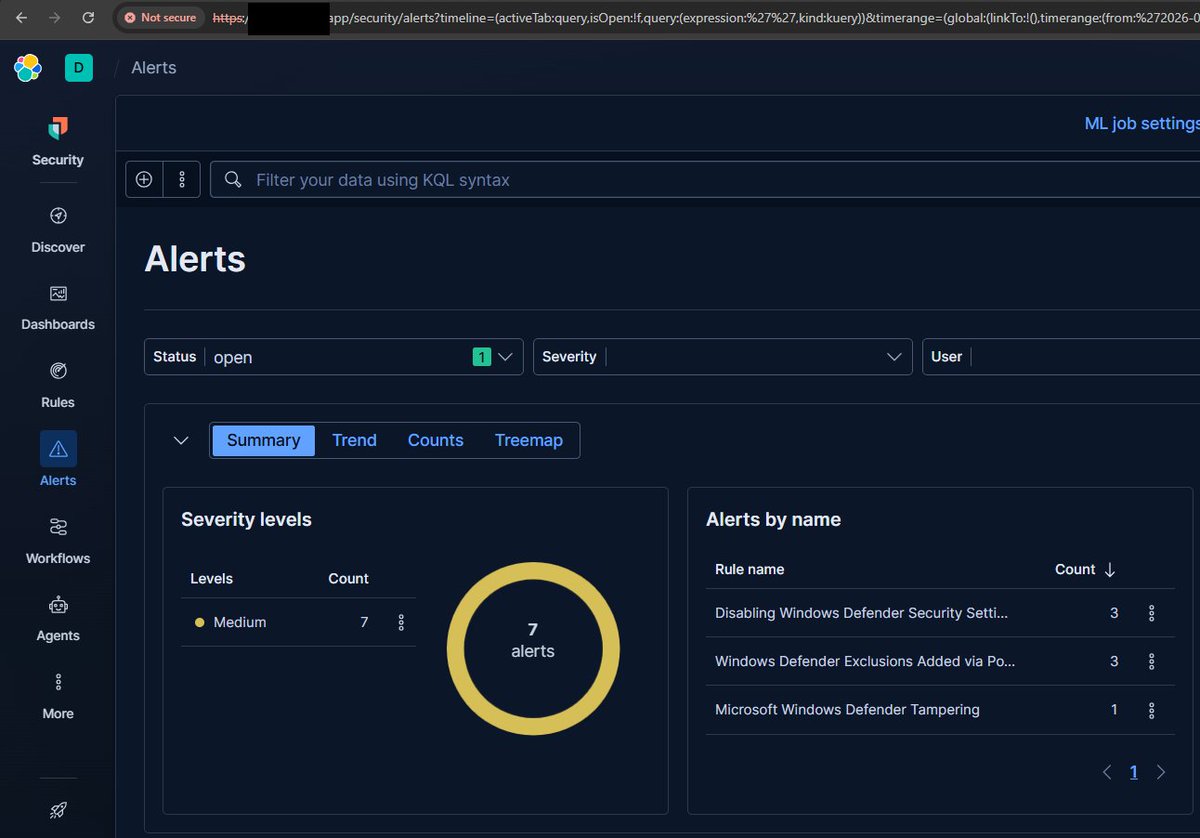
There are plenty of ways to build a detection lab, but elastic-container is the fastest Elastic stack setup I know. One script gives you: - Elasticsearch + Kibana + Fleet - Detection Engine on, prebuilt rules bulk-enabled by OS - 100% containerized, one command up or down Have Claude or Codex set it up for you. Credit: Andrew Pease (@andythevariable). github.com/peasead/elasti…
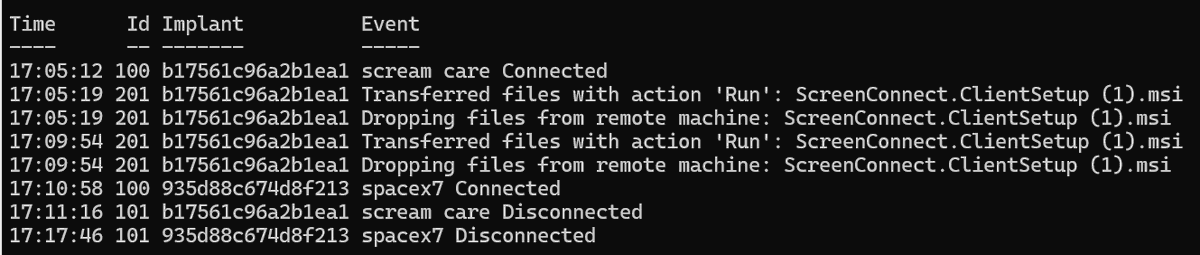
Ever closed a ScreenConnect case on EDR timestamps alone? My EDR's last event on the operator: 17:09. The product's own Application log had them working until 17:17. Get-WinEvent -FilterHashtable @{LogName='Application'; ProviderName='ScreenConnect'; Id=100,101,201} | Sort-Object TimeCreated | fl TimeCreated, Id, Message - 100/101 = operator connect/disconnect with session label - 201 = file transfer. Two implants on one box: scream care, then spacex7. A 4 min incident was 12 min.
BlackFile shut down in May. The crew is still in play as Redact, Pink, Helix and Falcon. Helpdesk call to your personal phone, then a "passkey enrolment" AiTM page. EDR sees nothing. 3 identity tells (GTIG): - MFA factor registered right after abandoned pushes - UAL FileAccessed from a python-requests / PowerShell UA - SSO sign-in via commercial VPN or residential proxy cloud.google.com/blog/topics/th…
@SwiftOnSecurity Thanks. Happy to hear your feedback or suggestions when you get to it 😊
Ever closed an RMM alert because the tool was sanctioned? Stop hunting AnyDesk by filename. Rank it by how rare it is across your fleet. A sanctioned tool is everywhere. A renamed copy on 1 host is the lead, even as Invoice_Viewer.exe still carrying AnyDesk's PE metadata. Full case, 32 ransomware groups and why your EDR sees a legit tool, in my Article below. 🔎

One process. 254 IPs. 5 ports. One time window. That's a network sweep, and the binary name never entered the logic. A dcount threshold on DeviceNetworkEvents catches Advanced IP Scanner, Advanced Port Scanner, and NetScan the same way. Signature-free 🔎

@Kostastsale @ThruntingLabs Thank you, will try. Lol 😆
Been testing GPT-6 Astra against some recent malware we collected through IR engagements. I used the ChatGPT Chrome extension with Guacamole running a @ThruntingLabs FlareVM environment directly inside the browser. Samples included a recent SynkLoader, SystemBC and a few fairly nasty obfuscated DLLs. Using high effort, Astra got through the analysis in roughly 15 minutes and found pretty much everything I was looking for, including obfuscated configuration, encrypted passwords embedded in the binaries and the important execution behaviour. That part impressed me, but overall, computer use is insane! Compared with GPT-5.6 Sol, the difference is huge. Astra was much better at understanding what was on screen, interacting with the tooling and moving through the analysis without getting lost. This changes the automation angle quite a bit. You can now start thinking about automating workflows around the actual tools analysts already use, rather than having to rebuild everything around APIs and custom integrations. Just throw Computer Use at it and let it do the work. Very interesting direction for DFIR and malware analysis!


The best data point would be bytes sent, since this query is focused on data exfiltration. But I don't think MDE captures that field, so I wrote these queries to identify the initial infection instead. If you have another data source such as proxy logs, you may be able to correlate the initial MDE hit with that proxy data.
I'd recommend excluding ports 80 and 443, and focusing on the SFTP portion, whether that's the standard port 22 or a custom port used by the attacker. If this still returns too much data, I'll filter by IP after collecting basic WHOIS data. Let me know what you see. I hope this helps.
@thebluesec Yeah, it may generate noise but worth hunting as ransomware group uses filezilla for exfil.
Your FileZilla alert is buried under installer and auto-update traffic. Cut that chatter and one connection is left standing. 🔎 The vendor noise lives on 80/443. Filter it. What survives on a file server: fzsftp.exe to a public IP on a custom port (3333), non-IT user, outside change windows. That's the connection to triage.

One SSH tunnel made 302 connections. 296 of them failed. That's not a pivot, that's a subnet sweep. Two signals: destination cardinality and failure rate. A fixed forward holds one IP, one port, zero failures. A subnet sweep churns many IPs, many ports, successes and failures together. Same mechanism. Different shape. I reproduced all three in the lab and put the rows side by side. Full breakdown 👇


Florian Roth ⚡️ @cyb3rops
224K Followers 3K Following Head of Research @nextronsystems #DFIR #YARA #Sigma | detection engineer | creator of @thor_scanner, Aurora, Sigma, LOKI, YARA-Forge | always busy ⌚️🐇 | vi/vim
SwiftOnSecurity @SwiftOnSecurity
416K Followers 9K Following computer security person. former helpdesk.
Ali Hadi | B!n@ry @binaryz0ne
35K Followers 573 Following DFIR and Adversary Simulation | All posts reflect the views and interests of the person behind this account only |
Karsten Hahn @struppigel
26K Followers 783 Following MalwareAnalysisForHedgehogs, Principal Malware Researcher at GDATA, he/him 🦔🌈🏳️⚧️
Matthew @embee_research
14K Followers 2K Following Security Researcher, Creating and Sharing Educational Content.
Michael Koczwara @MichalKoczwara
25K Followers 2K Following Threat Researcher/Founder @Intel_Ops_io Threat Intelligence, Adversary Infrastructure Hunting, Curated TI Feed (Coming Soon) https://t.co/VQWaze6gaF
mRr3b00t @UK_Daniel_Card
126K Followers 8K Following Chief Artificial Intelligence Cyber Security Scientist Counter Brain Worms Collective Member former Helpdesk AI infection status: clean
Stephan Berger @malmoeb
30K Followers 1K Following Head of Investigations @InfoGuardAG https://t.co/A5lnFAu7eX
Josh Stroschein | The... @jstrosch
12K Followers 1K Following Reverse engineer and content creater | 😱 1M+ views on YT | 🎙️ Host of Behind the Binary podcast 👇
Kostas @Kostastsale
21K Followers 498 Following I like building things that solve real problems, working across cybersecurity, product, and research | 🇬🇷🇨🇦


Abraham Polishchuk @abepolishchuk
65 Followers 893 Following CTO @FidesiumApp - Cybersecurity Partner, Manual Audits, Pen Testing, DevSecOps, 50+ audits completed. Experienced Blockchain Auditor
ᎡᎪᏴᏴᎥᎢ @wrrcroot
0 Followers 162 Following Premature optimization is the root of all evil (or at least most of it) in programming. (Donald Knuth)
Gobisto @Sizwe_Goba_
244 Followers 2K Following Joker, Free thinker, Crazy sometimes, always willing to learn and evolve husband to my gorgeous wife 💍❤️
wBot @HongLuDianXue_
19 Followers 763 Following
dumyyys @dumyyyshzj
0 Followers 13 Following
s127 @dumdumcui8u
29 Followers 107 Following SOC Analyst 2024 ~ CTI・マルウェア解析を勉強中 公開サンプルの解析・攻撃チェーン・TTPを発信。 学習記録をZennで公開しています。
bryan @bryan51649522
0 Followers 156 Following
Pepo Root @mahmmoudel5ateb
157 Followers 829 Following RE isn’t just skill — it’s philosophy, persistence, and pattern recognition
Yasser Selima @yass54285
0 Followers 114 Following
林卡Linka @lnk151633844445
13 Followers 3K Following

Kusanagi @goldenpath1981
68 Followers 1K Following Human signals in synthetic noise • mostly self-taught, partly educated
pfransc @pfransces
43 Followers 2K Following
Adel LA @laoui_adel
16 Followers 266 Following
Eduardo Gualito @gualito_eduardo
0 Followers 1K Following
Zheray @SatelliteNetSec
8K Followers 6K Following 32 | Dad | ☭ l Spaceflight Cybersecurity, previously @Bungie, telecom security etc | Avid reader | History, Geopolitics, Tech | Opinions mine | 🇵🇸🇱🇧🇸🇩🇾🇪
Scott Lynch @packetengineer
2K Followers 5K Following Certified @SANSDefense Instructor | SECOPS/CERT Manager | Defcon BTV | Navy Vet | Sailor | Tweets Are My Own
steeb6 @mtittle1
1 Followers 502 Following
Chaminda Ranasinghe�... @chamindarr
486 Followers 5K Following #Servers #Networking #Windows #IT #Linux #Apple #Traveling #Microsoft #Etc
kljfdlkdskjfdsf @kljfdlkdsk36735
4 Followers 472 Following

DodgyDoge @AlexisWater6293
2 Followers 95 Following

ibraheem @ibraheem_a23
0 Followers 73 Following
Israel @israel2235
252 Followers 1K Following
aye @Nurulyasoniq1
0 Followers 442 Following

4nqul1 @4nhqny3u
2 Followers 41 Following

adam @heavenappealer
5 Followers 278 Following
rogerwignall @rogerwignall
19 Followers 7K Following
S1dhy @s1dhy
321 Followers 259 Following Malware & Phishing Threat Hunter | Cybersecurity Enthusiast | Passionate about exposing digital threats and protecting online spaces | #Infosec #ThreatHunting
Yannick Boog @YannickBoog
62 Followers 6K Following
1t 1s N0b0dyh 🏴... @1t1sNobody
482 Followers 3K Following Sometimes I tweet something! Fighting and studying #malware in the other time

Colum Ó Ceallacháin @columocallaghan
147 Followers 2K Following Republican to the end,Full stack RoR Dev, political activist. Outdoorsy, books & the Med, runner, cyclist and stubborn optimist. Feed me tech news.
shiba @shiba15182
39 Followers 389 Following
Chiheb @BTCTN210
11 Followers 445 Following إن التاريخ في ظاهره لا يزيد عن الإخبار، و لكن في باطنه نظر و تحقيق. #ابن_خلدون 📚
Evild3ad79 @Evild3ad79
1K Followers 420 Following
Junet Medina @JunetMedina
30 Followers 250 Following
teio @teio1515599
24 Followers 2K Following
Rohit Warghade @Roowarghade
0 Followers 66 Following Cyber Threat Intel | Football. Cricket. OSINT. Repeat.
Austin Scott @Austin_M_Scott
2K Followers 1K Following In search of industrial control system (ICS) cyber badness. Director of Detection in Intel @dragosinc
T33j @t33j_sec
19 Followers 153 Following
raman @raman__bat
0 Followers 44 Following
G859 @grady859
12 Followers 475 Following
Florian Roth ⚡️ @cyb3rops
224K Followers 3K Following Head of Research @nextronsystems #DFIR #YARA #Sigma | detection engineer | creator of @thor_scanner, Aurora, Sigma, LOKI, YARA-Forge | always busy ⌚️🐇 | vi/vim
vx-underground @vxunderground
449K Followers 375 Following The largest collection of malware source code, samples, and papers on the internet. Password: infected
SwiftOnSecurity @SwiftOnSecurity
416K Followers 9K Following computer security person. former helpdesk.
Alexandre Borges @ale_sp_brazil
32K Followers 181 Following Exploit Developer and Vulnerability Researcher
MalwareHunterTeam @malwrhunterteam
257K Followers 39 Following Official MHT Twitter account. Check out ID Ransomware (created by @demonslay335). More photos & gifs, less malware.
ςεяβεяμs - м�... @c3rb3ru5d3d53c
27K Followers 243 Following 💕 Malware Reverse Engineer & Malware Geneticist 💕 #Binlex Developer https://t.co/EKYUS9Itvd 👩💻 She/Her
Ali Hadi | B!n@ry @binaryz0ne
35K Followers 573 Following DFIR and Adversary Simulation | All posts reflect the views and interests of the person behind this account only |
Jiří Vinopal @vinopaljiri
11K Followers 633 Following Security Researcher at @_CPResearch_ All opinions expressed here are mine only. https://t.co/bNWc3k9HwF
Karsten Hahn @struppigel
26K Followers 783 Following MalwareAnalysisForHedgehogs, Principal Malware Researcher at GDATA, he/him 🦔🌈🏳️⚧️
Matthew @embee_research
14K Followers 2K Following Security Researcher, Creating and Sharing Educational Content.
John Hammond @_JohnHammond
326K Followers 3K Following Cybersecurity Researcher @HuntressLabs Just Hacking Training @JustHackingHQ w/ @ethicalhacker https://t.co/UtsNJiyQtS && https://t.co/narO3sz7y6

Justin Elze @HackingLZ
74K Followers 5K Following CTO @TrustedSec | Former Optiv/SecureWorks/Accuvant Labs/Redspin | Race cars
Michael Koczwara @MichalKoczwara
25K Followers 2K Following Threat Researcher/Founder @Intel_Ops_io Threat Intelligence, Adversary Infrastructure Hunting, Curated TI Feed (Coming Soon) https://t.co/VQWaze6gaF
Thomas Roccia 🤘 @fr0gger_
35K Followers 2K Following Founder @SecurityBreakAI AI Security x Threat Intel · Threat Researcher · Creator of #Unprotect & #NOVA · Python 🧡 · Prev @Microsoft @McAfee_Labs
hasherezade @hasherezade
91K Followers 968 Following Programmer, #malware analyst. Author of #PEbear, #PEsieve, #TinyTracer. Private account. All opinions expressed here are mine only (not of my employer etc)
blackorbird @blackorbird
44K Followers 703 Following Peace and Love. Just Analysis/Hunter/Youtuber/AiCoder/Entrepreneur/. #APT #threatIntelligence #Exploit #CTI #meme #cyber #hacker #OSINT #Ai Need Remote Job
marc ochsenmeier @ochsenmeier
14K Followers 72 Following Malware Analyst @BoschGlobal CERT | Author of #pestudio
mRr3b00t @UK_Daniel_Card
126K Followers 8K Following Chief Artificial Intelligence Cyber Security Scientist Counter Brain Worms Collective Member former Helpdesk AI infection status: clean
Stephan Berger @malmoeb
30K Followers 1K Following Head of Investigations @InfoGuardAG https://t.co/A5lnFAu7eX
Scott Lynch @packetengineer
2K Followers 5K Following Certified @SANSDefense Instructor | SECOPS/CERT Manager | Defcon BTV | Navy Vet | Sailor | Tweets Are My Own
Censys @censysio
13K Followers 1K Following Censys is the authority in Internet intelligence & insights. Delivering the most comprehensive, accurate, and up-to-date global map of Internet infrastructure.
Dave Kennedy @HackingDave
233K Followers 6K Following Founder @Binary_Defense @TrustedSec Co-Owner https://t.co/NUvgPUifL0. @WeHackHealth Pod. God + Family/Hacker/CSO/USMC/Intel/Fitness. Make the world a better place.
SOS Intelligence @SOSIntel
20K Followers 2K Following Dark Web Intelligence. We find what's been stolen before it's weaponised. https://t.co/aQgEdlJVPl
Germán Fernández @1ZRR4H
39K Followers 467 Following 🏴☠️ OFFENSIVE-INTEL 🏴☠️ Cyber Threat Intelligence by Hackers | Security Researcher at https://t.co/rDrSxZStZD | @CuratedIntel Member | 🥷🧠🇨🇱
Kirk @KirkDerpca
332 Followers 275 Following Kirk from https://t.co/yKnARcddwy Security Research - We like the internet. @adam_networks

Claude Code Changelog @ClaudeCodeLog
82K Followers 20 Following UNOFFICIAL – but tolerated – bot posting Claude Code CLI, feature flag & prompt changes. Full CC history in github repo.

Contabo @ContaboCom
12K Followers 2K Following Cloud server provider | Fair priced VPS and Bare Metal | Data Centers in 🇪🇺 🇺🇸 🇬🇧 🇸🇬 🇦🇺 🇯🇵| 20+ years of experience | 200K+ happy customers
Bohan Zhang @bohansec
2K Followers 4K Following Threat Intelligence Researcher @esthreat 🚀🚀| Blue Teamer
Jack Rhysider 🏴... @JackRhysider
172K Followers 4K Following Creator of @DarknetDiaries and @LOWpodcast. Tell me a good hacker story. 💻🔦⤵️🐰🕳️ Discord: https://t.co/qxanMuIy7u
Dirk-jan @_dirkjan
30K Followers 208 Following Hacker at @OutsiderSec. Researches AD and Azure (AD) security. Likes to play around with Python and write tools that make work easier.
Nathan McNulty @NathanMcNulty
19K Followers 1K Following Loves Jesus, loves others | Husband, father of 4, security solutions architect, love to learn and teach | Microsoft MVP | @TribeOfHackers | 🦋@nathanmcnulty.com
OccupytheWeb @three_cube
269K Followers 3K Following Pentester, Forensic investigator, and former college professor. Trained hackers at each US military and intelligence. Visit me at https://t.co/G478wug0p4
Jose Enrique Hernande... @_josehelps
4K Followers 2K Following ⚔️Prevention Engineering @MagicSwordIO | Ex-@Splunk Threat Research Dir. | Co-creator #LOLDrivers #LOLRMM | Maintainer #AtomicRedTeam #LOLBAS 🤿
cr0@Defensive-Securit... @cr0nym
3K Followers 3K Following Focus on Linux/Kubernetes Attack/Detection/Forensics/Incident Response/Threat Hunting/Active Defense. Learning hard every single day.
Typefully @typefully
42K Followers 7 Following Join 200k+ creators to write, schedule & publish on 𝕏 and LinkedIn, without distractions • Now with AI ✨
OIHEC hackers @HackersOIHEC
47K Followers 16K Following Hacker mexicano - Fundador de OIHEC antes OMHE - #opensoc #latam #speaker #pentester #blueteam #redteam #criptoanarquista #security
Luke Acha @luke92881
507 Followers 359 Following Incident Response and Malware Detection enthusiast.
spencer @techspence
18K Followers 3K Following 🛠️ Former Sysadmin, now Pentester | Microsoft MVP | Helping IT teams make their environment harder to attack | @SecurIT360 & @CyberThreatPOV
Logesh @logesh0210
15 Followers 286 Following
Mark Manson @Markmanson
784K Followers 127 Following #1 New York Times Bestselling Author of five books, including "The Subtle Art of Not Giving F*ck". Co-Founder of @Purpose_AI. Host of Solved Podcast.
Ronin @DeRonin_
118K Followers 871 Following 20 / CEO of Arcane / Angel Investor / engineering virality for AI companies
Matt Pocock @mattpocockuk
353K Followers 809 Following I teach devs for a living. Author of Total TypeScript and AI Hero. Ex-@vercel. Used to be a voice coach.
JK Molina @OneJKMolina
239K Followers 191 Following Co-Founded Tweet Hunter. Sold for $8 million. Reducing coaches' and agencies' churn by half through giving them software they own (DFY).
Charlie Eriksen @CharlieEriksen
4K Followers 429 Following Security Researcher @AikidoSecurity. Previously @SecCodeWarrior, co-founder at Adversaryio & Principal Security Engineer/Partner @thesyndis. Opinions all my own
Soumyani1 @reveng007
1K Followers 2K Following Red mind. Blue mission. Turning attack tradecraft into detections | CARTE | CRTO | CRTP | @BlackHatEvents Arsenal, @WWHackinFest and @BSidesSG Presenter
ᴍɪᴄʜᴀʟɪs �... @Cyb3rMik3
4K Followers 3K Following Regional Threat Protection Tech Lead @Microsoft | Former Microsoft MVP | Father 👭/Husband👫/🍷&⌚️ enthousiast/Explorer ✈️ | Views my own.
Andy Gill @ZephrFish
20K Followers 665 Following Security Researcher, RT, Director & Course Author at @ZephrSec |Staff on @CuratedIntel | Lab Creation @XintraOrg | https://t.co/gvGwReANzD - check out my RT course
Aura @SecurityAura
6K Followers 680 Following GCIH, GCFE, GDAT | DFIR, TH, DE | @CuratedIntel DFIR https://t.co/BMWUwziTLh https://t.co/MmX2YNVqdk https://t.co/R20zseQfLk
Socket @SocketSecurity
23K Followers 5K Following Socket is the #1 software supply chain security platform. Next-gen SCA + SBOM + 0-day prevention. LOVED BY DEVELOPERS. 👀 @npm_malware
Fabian Bader @fabian_bader
11K Followers 907 Following #Security #Azure #AAD #MDE #M365 #AD #PKI #XDR #EntraID Microsoft MVP Tweets and opinions are my own @[email protected]
Elastic @elastic
66K Followers 184 Following Where developers learn, build, and share. Your source for hands-on demos, cheat sheets, explainers and more.
Sean Metcalf @PyroTek3
37K Followers 710 Following Identity Security Architect @ TrustedSec. Microsoft Certified Master #ActiveDirectory & former Microsoft MVP. Co-Host @ Enterprise Security Weekly. He/Him. #BLM
Julien | 🦋@julien.... @JMousqueton
2K Followers 562 Following Field CISO at @cohesity | owner of https://t.co/mcCsqeRJaO | | Lecturer at @Ecole2600 🏴☠️
Tim Blazytko @mr_phrazer
6K Followers 264 Following Binary Security Researcher & Trainer | PT Chief Scientist @ Emproof Also at https://t.co/YBfgAt3kc7
Dark Web Informer @DarkWebInformer
239K Followers 92 Following One guy. Global cybercrime. Tracked so you don't have to. Ransomware, data breaches, dark web activity, darknet markets, IOCs & emerging threats. Stay informed!
BriPwn @BriPwn
1K Followers 448 Following Cybersecurity Professional | MSISE, GIAC x16, CISSP-ISSAP, CISM | SANS Certified Instructor
Zach @svch0st
4K Followers 1K Following Everything DFIR @TheDFIRReport | @CuratedIntel | @XintraOrg https://t.co/ggakuKBS0S
Renzon @r3nzsec
5K Followers 930 Following IR/Forensics @Unit42_Intel | Contributor/Analyst @TheDFIRReport @XintraOrg | Co-Founder @guidemtraining | CTF member @_hackstreetboys

Panos Gkatziroulis �... @ipurple
27K Followers 825 Following Red/Purple Teamer | Blogger | Mod @ https://t.co/f4RyUGl0zb | https://t.co/nLrzzAcQw9
InfoGuard Labs @InfoGuard_Labs
301 Followers 1 Following Insights from the frontlines of offensive security and incident response @ https://t.co/uMKNWv9KUy
Giuseppe `N3mes1s` @N3mes1s
14K Followers 336 Following windows, macos, linux, android && lowlevel && ring-1 lover; EDR chef; malware hunter; purple team💜
Will @BushidoToken
39K Followers 3K Following Senior Threat Intel Advisor @TeamCymru Co-founder @CuratedIntel Co-author @SANSForensics FOR589 Co-founder @BSidesBournemth #126: REvil @darknetdiariesYou might like