DefSecSentinel @DefSecSentinel
Staff Threat Detection Engineer @Chainalysis and 179CPT Cyber Operations Technician 170A @MOARNG Joined April 2017-
Tweets621
-
Followers2K
-
Following1K
-
Likes16K

🏈 Calling the infosec community! We had a spot open up to round out Year 4 of the "Secure the Ball" fantasy football league. If you love to talk shop, ball, and trash - join us! ⚠️ There are punishments 🙋🏻♂️ DM me for details #infosecfantasyfootball #fantasyfootball
Calling all football fans! I'm thinking of running an infosec fantasy football league. I know it's cutting it close, we would need to draft before Thursday. Is anyone interested? DM me your email if you want in.
Just announced: talks for #OBTS v9 🥳 Stoked on an epic lineup of cutting-edge 🍎- security research, covering exploitation, malware, reversing, security tools, AI, & more! Check out the full lineup: objectivebythesea.org/v9/talks.html Which one(s) are you most looking forward to!? 🤔

Elastic Defend 9.5.0 now carries the taint state on Linux kernel module loading events. I loaded Singularity (the stealthiest open source rootkit I know). On load, it hides from lsmod, /proc/modules, and /sys/module, resets the kernel taint mask to 0, and filters "taint" and its own name out of dmesg, journalctl -k, and klogctl. Even though the system looked clean, detecting the tainted flag on the loading event already exposed it. What is even more suspicious? The endpoint recorded this module loading out-of-tree and unsigned. The live host says the mask is 0, and taint is sticky by design, so that needs explaining and is a good hunting reference. One caveat, because this is not a rule to switch on blind: OE is also what a DKMS build, an out-of-tree GPU driver, or a third-party filesystem module produces. Baseline the modules you load on purpose, then investigate what is left. Enforcing module signatures shrinks it further, since an unsigned module then fails to load. Rule PR and references in the reply. #Linux #DetectionEngineering #ThreatDetection #DFIR #Rootkits


Seen in the wild in REF6138. Full teardown, including the kernel-process masquerade and the detections: elastic.co/security-labs/… Rules that fire: • Executable Masquerading as Kernel Process: github.com/elastic/detect… • Process Masquerading as Kernel Process (Defend): github.com/elastic/protec… • Network Activity Detected via Kworker: github.com/elastic/detect…

@SBousseaden and I did some investigations into Tycoon 2FA recently. Focused on the infrastructure, how the kit works for not only M365, but Google Workspace as well. Made a few detections for each platform. Give it a read. Hope you enjoy. #phishing #threatdetection Happy Hunting! elastic.co/security-labs/…
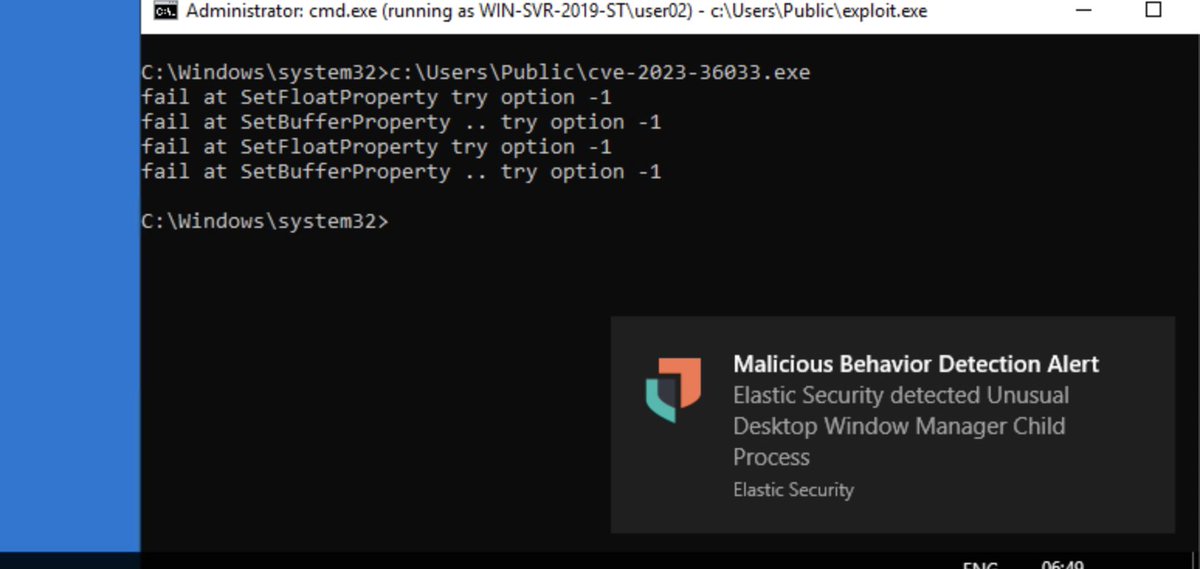
MiniPlasma LPE exploit works perftectly. Elastic Defend behavior protection catches the exploit primitives involved in the chain, providing detection coverage even against fresh public exploit. github.com/Nightmare-Ecli…

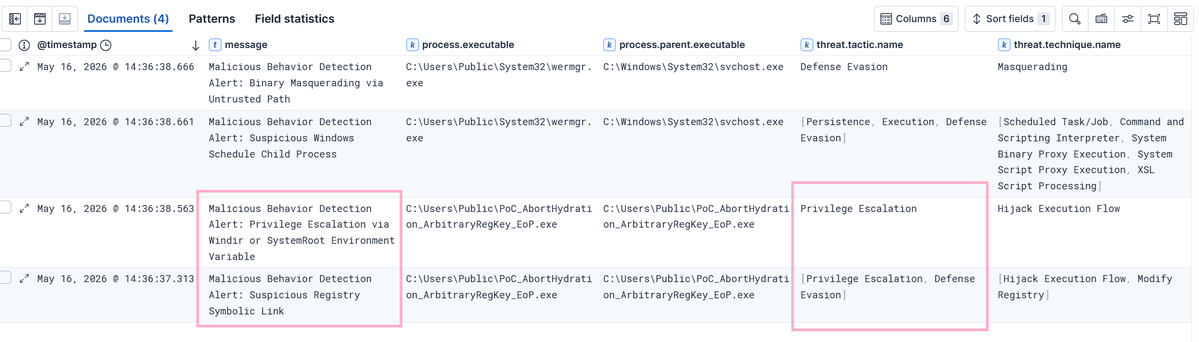
We just posted some additional detection guidance for #CopyFail and #DirtyFrag using EQL, ES|QL and Auditd detection rules/hunts + mitigations. Find them below! elastic.co/security-labs/…
New DirtyFrag PoC is also detected by our previously released Linux privilege escalation detection👀 That’s the advantage of focusing on the underlying privilege escalation pattern instead of a single exploit. You can find the rule here: github.com/elastic/detect…
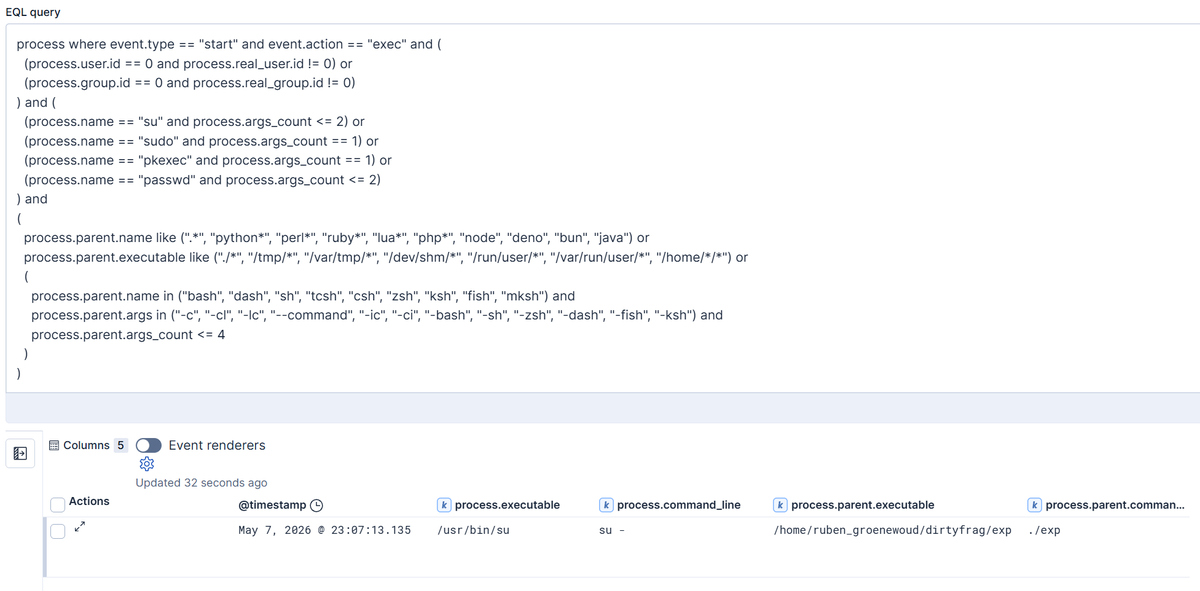
Detection guidance for CopyFail (CVE-2026-31431) and DirtyFrag (ITW Linux page cache LPE): EQL, ES|QL, and auditd detection rules and hunts included: elastic.co/security-labs/…
Yesterday was my last day at @elastic. It was an incredible run. I’m grateful for the opportunity I was given to help build Elastic’s #macOS endpoint agent and endpoint/SIEM detections from the ground up, work that delivered real impact for customers and made life harder for the adversaries. It was truly an honor to work alongside so many talented people, and I’m very proud of everything we built together. Wishing Elastic and everyone there nothing but the best. I’ll be looking for my next adventure soon. Stay tuned!
good to see EXISTING Elastic generic privesc behavior detection/protection triggering on the RedSun LPE exploit with no prior knowledge of the vuln-details. github.com/elastic/protec…
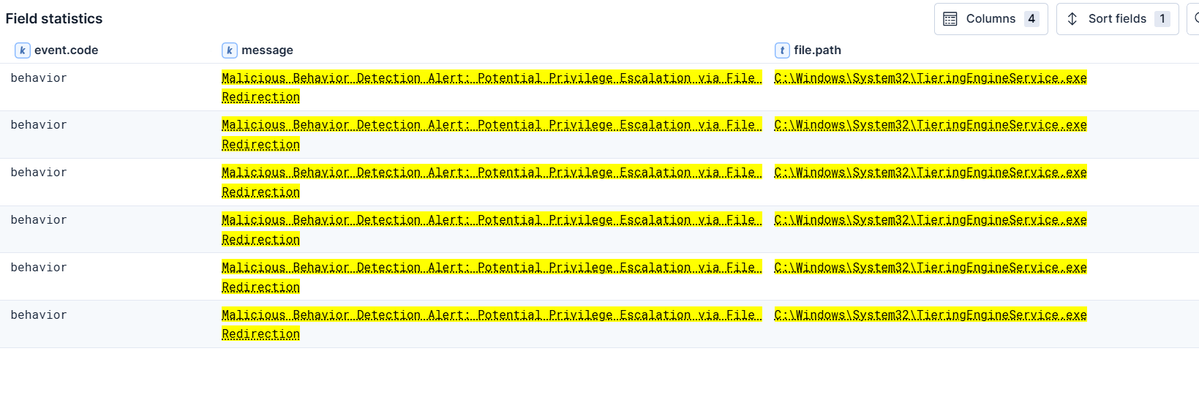
New blog post is up, exploring detection options for some recent In- the- Wild Windows LPE 0- days elastic.co/security-labs/…

google workspace logs from reports API... here's a simple query (Elastic) to check for the vercel 3rd-party OAuth app auth event: ``` data_stream.dataset: "google_workspace.token" and event.action: "authorize" and google_workspace.token.client\.id: 110671459871-30f1spbu0hptbs60cb4vsmv79i7bbvqj.apps.googleusercontent\.com ``` from there, the same app ID shows up in a few other GWS fields/datastreams: - token\.app_name -> human-readable app label - drive.originating_app_id: 110671459871 -> every file the app viewed/downloaded/copied (prefix only, it's typically the GCP project number IIRC) - admin.oauth2.application\.id / .name -> admin-side OAuth approvals + domain-wide delegation grants for everything else (gmail, login, meet, chat, calendar, groups, DLP rules) I'd try actor pivot on source.user.\email + a time window around the consent event (reports API can lag up to 3 days, so go wide and check ingestion). good luck hunters! #Vercel #GoogleWorkspace #threathunting
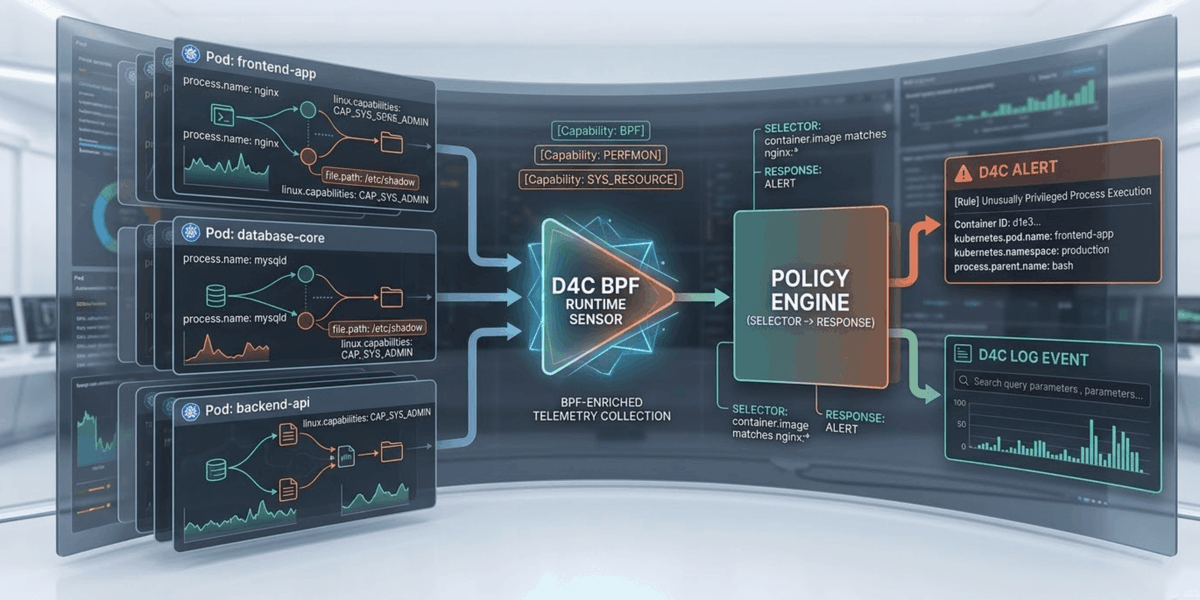
Attackers in containers don't leave persistent artifacts. No files on disk. No post-incident logs. Just short-lived runtime behavior. Traditional detection approaches weren't built for this. Defend for Containers is. @RFGroenewoud published a deep-dive on how D4C captures runtime signals inside containerized Linux workloads, and how to build detection logic on top of it. The key things D4C gives you that you don't get elsewhere: - process.interactive flags hands-on-keyboard activity in production containers — rare and high-signal - Linux capability fields (effective + permitted) let you assess actual exploit potential, not just process names - Every event enriched with pod name, namespace, cluster, and privilege context - Policy wildcards let you scope detections to specific images, namespaces, or directory trees go.es.io/48sPCtC
You are going to want to check out this awesome new research write-up from the team. Very interesting and somewhat creative initial access method. Includes a @macos piece as well. Shout out to @soolidsnakee, @SBousseaden and team working hard to get this out.
We have identified a novel social engineering campaign abusing Obsidian, the popular note taking app, to deliver a previously undocumented RAT #PHANTOMPULSE and it’s loader #PHANTOMPULL targeting individuals in finance and crypto. The attack never exploits a vulnerability. It
New #research together with @SBousseaden and @DanielStepanic at @elasticseclabs. We uncovered a campaign abusing Obsidian plugins and vault feature to deliver multi-platform payloads targeting both #Windows and #macOS. The final stage is #PHANTOMPULSE, an AI-built RAT that resolves its #C2 from Ethereum blockchain transactions and its loader #PHANTOMPULL A deep dive into the RAT internals is coming next. Stay tuned. elastic.co/security-labs/…
We have identified a novel social engineering campaign abusing Obsidian, the popular note taking app, to deliver a previously undocumented RAT #PHANTOMPULSE and it’s loader #PHANTOMPULL targeting individuals in finance and crypto. The attack never exploits a vulnerability. It abuses Obsidian's own plugin ecosystem to execute code the moment a victim opens a shared vault. Full analysis: go.es.io/4cld0dB
Not every “old” GitHub repo is actually old. I break down DPRK-linked repo tradecraft abusing commit-date spoofing to fake legitimacy, while hiding obfuscated loaders in trusted config files. One sample had 100+ stars. Research: kl4r10n.tech/blog/when-git-… Thanks @pcaversaccio for recreating the spoofed commit and helping validate the technique.

It seems possible that clickfix malware is already switching tactics to evade the new Terminal copy/paste security feature in macOS 26.4.
ClickFix techniques are evolving. Instead of copy and paste instructions to Terminal, newer variants are using Script Editor to execute payloads on macOS. Read more about this delivery technique in our latest blog post. jamf.com/blog/clickfix-… #clickfix #malware #threathunting

Florian Roth ⚡️ @cyb3rops
224K Followers 3K Following Head of Research @nextronsystems #DFIR #YARA #Sigma | detection engineer | creator of @thor_scanner, Aurora, Sigma, LOKI, YARA-Forge | always busy ⌚️🐇 | vi/vim
Justin Elze @HackingLZ
74K Followers 5K Following CTO @TrustedSec | Former Optiv/SecureWorks/Accuvant Labs/Redspin | Race cars
Samir @SBousseaden
26K Followers 1K Following security/detection-eng @Elastic Mastodon: @[email protected]
SwiftOnSecurity @SwiftOnSecurity
416K Followers 9K Following computer security person. former helpdesk.
mRr3b00t @UK_Daniel_Card
126K Followers 8K Following Chief Artificial Intelligence Cyber Security Scientist Counter Brain Worms Collective Member former Helpdesk AI infection status: clean Task Force 29
Andrew Thompson @ImposeCost
42K Followers 2K Following SVP of Adversary Operations @GreyNoiseIO. Former @USMC and @Mandiant. There's no finish line in security.
ippsec @ippsec
125K Followers 372 Following
Daniel Stepanic @DanielStepanic
1K Followers 645 Following Malwarez at @elasticseclabs | Macrodata Refinement
Nasreddine Benchercha... @nas_bench
12K Followers 1K Following Detection @Splunk & @cisco | previously @nextronsystems | @sigma_hq & @magicswordio maintainer | Eternal Learner

Tony Lambert @ForensicITGuy
6K Followers 1K Following Recovering sysadmin that now chases adversaries instead of uptime. Sr Malware Analyst @redcanary
Adam Chester 🏴�... @_xpn_
39K Followers 554 Following TRACE at @SpecterOps | Blog at https://t.co/tjfTOllCEu
Silas Cutler (p1nk) @silascutler
14K Followers 2K Following You may know me from your logs Principal Security Researcher @Censysio #Threats / #CTI / #Malware / #Hacking
James @jamesspi
1K Followers 536 Following Helping folk do security things with @elastic. Views are my own. Creator of https://t.co/FY2IQ2eAhe, https://t.co/aDuzYgUuYw, https://t.co/qz9J8Kb0v3 and https://t.co/eiiVHgqb5G
Jonny Johnson @JonnyJohnson_
9K Followers 454 Following Windows Internals & Telemetry Research Sr. Manager @btphantomlabs Host: @ThePayloadPod Blog: https://t.co/MnE9BCsky2 Github: https://t.co/v7hSLq66o1
Jaron Bradley @jbradley89
3K Followers 301 Following MacOS Intrusion Analyst, APT Smiter , Haole. Author of OS X Incident Response Scripting and Analysis Owner of https://t.co/oApHpiRaQ0

M @Unpainted4802
0 Followers 801 Following
daniel @c1um3y
0 Followers 5 Following
Beate Klatschfeld @c_qkie
45 Followers 3K Following Ohrfeigen möchte ich meinen zarten Wurstfinger trotzdem nicht antun
P5y09s @TheLastPiv0t
33 Followers 1K Following
XTM @0A1ZX
13 Followers 210 Following
Hector @HecSec256
1 Followers 88 Following
Levon Azevedo @Blackicelabs
52 Followers 550 Following IT Project Manager | Cloud, DevOps & Cybersecurity | MSc UCD Dublin | Founder ×2 (Acquired)


packetspoofer.bsky.so... @packetspoofer
6 Followers 988 Following #ThreatHunting #ReverseEngineering #BinaryExploitation #CriticalThinking #Books
lunaangel fka angel �... @lunahoneyk7wkm
38 Followers 1K Following dreamy vibe, too pretty to argue with mind ☁️
Prismor @prismor_dev
671 Followers 954 Following Open Source and Independent Control Plane for AI agents
Karthikeyan CB @karthikeyan_cb
19 Followers 1K Following
Magno Logan @magnologan
3K Followers 5K Following Information Security Specialist, International Speaker and Instructor at GoHacking, Biohacker and Novice powerlifter.
Caio @clivoa
110 Followers 3K Following
Bhabesh @bh4b3sh
453 Followers 617 Following Cybersecurity Analyst | Detection Engineer | Threat Hunter #Microsoft365 #EntraID #Azure #Windows #AD #AWS #Kubernetes
Parsa @L1L2core
0 Followers 81 Following
tmovuevuevue @tmovuevuevue
0 Followers 33 Following
lilbits @aishlop
1 Followers 51 Following
soso @donsovic
31 Followers 78 Following
Jeremy Thomas @dkjayce
25 Followers 126 Following
//// @QssvacntNJ14612
1 Followers 90 Following
BadHideApeSeek @0xReaper0x
484 Followers 1K Following Bad hide in logs. Ape follow tracks. Ape find. | #ArmyVet | Blue Team
Ron Gutani @RGutani
1 Followers 41 Following
cl4ire17 @snake448
72 Followers 1K Following seeking someone to do errands with. that is my love language
Z @Reyken0
0 Followers 35 Following
Anderson Vieira @andersonv3
291 Followers 1K Following Cyber Security | Hardware Hacking | 318br Team

Sebastian Torres @sebacornell
18 Followers 817 Following
PierreM @eG9kdXM
0 Followers 8 Following
Gary @clownbagz
183 Followers 966 Following Hunting vulnerabilities across crypto, cloud, and distributed systems. Interested in exploits, protocol design, and adversarial thinking.
Mahmoud @MahmoudSoheem
0 Followers 387 Following
AbuMuslim (أبومُ... @m19o__
11K Followers 3K Following Security nerd with a mic. Co-Founder @BSides_ABQ. Board @OWASPEgypt. R&D @aivillage_dc. YT @CyberDose_. Doing ai security somethere.
Cryptanalyst @Cryptanalyst19
431 Followers 5K Following Exploit writer, Threat Intel and a crypto guy.
SHIMIZU Taku @takuan_osho
2K Followers 4K Following Software Engineer (Primary language is Python) / Japanese Anime Fan(I love Zegapain!!!) / Practicing Budos(Iaido and Karate)
Miteak Pruteanu @MiteakPruteanu
2 Followers 65 Following
ritian zhao @ritianzhao15
5 Followers 468 Following


Blaze @atheosblazezero
18 Followers 913 Following
G33M @goddiemang
3K Followers 5K Following First of His Name, The Fixer of Things and Protector of the Unknown Realm
H. @0x485342c4b0
73 Followers 1K Following
Florian Roth ⚡️ @cyb3rops
224K Followers 3K Following Head of Research @nextronsystems #DFIR #YARA #Sigma | detection engineer | creator of @thor_scanner, Aurora, Sigma, LOKI, YARA-Forge | always busy ⌚️🐇 | vi/vim
vx-underground @vxunderground
449K Followers 375 Following The largest collection of malware source code, samples, and papers on the internet. Password: infected
Justin Elze @HackingLZ
74K Followers 5K Following CTO @TrustedSec | Former Optiv/SecureWorks/Accuvant Labs/Redspin | Race cars
Dave Kennedy @HackingDave
233K Followers 6K Following Founder @Binary_Defense @TrustedSec Co-Owner https://t.co/NUvgPUifL0. @WeHackHealth Pod. God + Family/Hacker/CSO/USMC/Intel/Fitness. Make the world a better place.
Elastic @elastic
66K Followers 184 Following Where developers learn, build, and share. Your source for hands-on demos, cheat sheets, explainers and more.
Samir @SBousseaden
26K Followers 1K Following security/detection-eng @Elastic Mastodon: @[email protected]
SwiftOnSecurity @SwiftOnSecurity
416K Followers 9K Following computer security person. former helpdesk.
mRr3b00t @UK_Daniel_Card
126K Followers 8K Following Chief Artificial Intelligence Cyber Security Scientist Counter Brain Worms Collective Member former Helpdesk AI infection status: clean Task Force 29
Andrew Thompson @ImposeCost
42K Followers 2K Following SVP of Adversary Operations @GreyNoiseIO. Former @USMC and @Mandiant. There's no finish line in security.
Katie Nickels @likethecoins
55K Followers 3K Following Director of Intel at @redcanary. SANS Certified Instructor for FOR578: CTI. Senior Fellow at @CyberStatecraft. She/her. Mastodon: @[email protected]
SANS DFIR @sansforensics
112K Followers 104 Following The world's leading Digital Forensics and Incident Response provider. This feed updates you on latest DFIR news, events, and training.
Mehmet Ergene @Cyb3rMonk
14K Followers 457 Following Teaching Threat Hunting, Detection Engineering, and KQL https://t.co/uAlYlXIpyV @BluRavenSec Microsoft Security MVP #ThreatHunting #DataScience
ippsec @ippsec
125K Followers 372 Following
Chris Sanders 🔎 �... @chrissanders88
36K Followers 488 Following Ed.D. | Founder @networkdefense @RuralTechFund | Former @Mandiant, DoD | Author: Intrusion Detection Honeypots, Practical Packet Analysis, Applied NSM

Florian Hansemann @CyberWarship
89K Followers 46 Following Father, Founder @HanseSecure, Pentesting, Student, ExploitDev, Redteaming, InfoSec & CyberCyber; -- Mastodon: https://t.co/KFSKYUN98M
Thomas Roccia 🤘 @fr0gger_
35K Followers 2K Following Founder @SecurityBreakAI AI Security x Threat Intel · Threat Researcher · Creator of #Unprotect & #NOVA · Python 🧡 · Prev @Microsoft @McAfee_Labs
John Hammond @_JohnHammond
326K Followers 3K Following Cybersecurity Researcher @HuntressLabs Just Hacking Training @JustHackingHQ w/ @ethicalhacker https://t.co/UtsNJiyQtS && https://t.co/narO3sz7y6
FBI Cyber Division @FBICyberDiv
20K Followers 69 Following Official FBI Cyber Division X. Submit tips at https://t.co/YZeSVuoxZI. Public info may be used for authorized purposes: https://t.co/is3HGZcnHx

Brandon Veiseh @BVeiseh
780 Followers 1K Following building safe autonomous pen testing | co-founder + ceo @mindfort (YC X25) - prev @netspi and @pdiscoveryio

Prismor @prismor_dev
671 Followers 954 Following Open Source and Independent Control Plane for AI agents
clem 🤗 @ClementDelangue
695K Followers 5K Following Co-founder & CEO @HuggingFace 🤗, the open and collaborative platform for AI builders

U.S. Central Command @CENTCOM
1.8M Followers 121 Following The official account of U.S. Central Command.
David Sacks @DavidSacks
1.8M Followers 4K Following Tech founder & investor @Craft_Ventures @theallinpod. Co-Chair, President’s Council of Advisors on Science & Technology.
@DoW_CIO @DoW_CIO
13K Followers 459 Following The official account of the U.S. Department of War Office of the Chief Information Officer. Linking, replying/following does not = endorsement.
Arcanum Information S... @arcanuminfosec
5K Followers 16 Following Expert Cybersecurity Training and Consulting by @jhaddix
MacSec Labs @MacSecLabs
387 Followers 17 Following Advanced hands-on macOS security training. Red team tradecraft, reverse engineering, exploitation & evasion. Built by operators, for operators

SpaceXAI @SpaceXAI
2.1M Followers 6 Following
Google Gemini @GeminiApp
577K Followers 53 Following The Gemini app turns research into reality, bringing frontier AI experiences like Omni, Deep Think, Nano Banana, and more to hundreds of millions of people.

Mistral AI @MistralAI
208K Followers 2 Following Frontier AI in your hands. Get work done with @MistralVibe at https://t.co/JsGnCVMUFq.
Pliny the Liberator �... @elder_plinius
241K Followers 1K Following ⊰•-•⦑ latent space steward ❦ prompt incanter 𓃹 hacker of matrices ⊞ breaker of markov chains ☣︎ ai danger researcher ⚔︎ bt6 ⚕︎ architect-healer ⦒•-•⊱
Microsoft Research @MSFTResearch
555K Followers 2K Following We advance science and technology to benefit humanity.

Armadin @ArmadinSecurity
542 Followers 16 Following Armadin is an AI-native cybersecurity company focused on building the ultimate attacker.
Nextron Research ⚡�... @nextronresearch
4K Followers 13 Following Nextron threat research team. Signatures, rules, and analysis focused on eliminating blind spots.
U.S. Cyber Command @US_CYBERCOM
144K Followers 255 Following Official Twitter page of U.S. Cyber Command (Following, retweets and links do not equal endorsement)
Paul Graham @paulg
5.3M Followers 799 Following
Permiso Security @permisosecurity
1K Followers 367 Following Detection for all of your clouds - identity providers, Iaas, Saas, Paas and more.
Cybersecurity and Inf... @CISAgov
327K Followers 106 Following America's Cyber Defense Agency and National Coordinator for Critical Infrastructure Security & Resilience. Likes, reshares, follows ≠ endorsements.
Y Combinator @ycombinator
1.7M Followers 367 Following We help founders make something people want. Subscribe to our newsletter: https://t.co/sjqjxxBeLc
DANΞ @cryps1s
18K Followers 513 Following CISO @OpenAI | Ex-CISO @PalantirTech | Occasional Shitposter | 🇺🇸 All views are my own, not my employer. Duh. (Tweets == 30d retention)

Tyler Bosmeny @bosmeny
9K Followers 666 Following Tyler: ('old engl'); One who tiles roofs. Co-Founder of @Clever. Now Partner at @YCombinator
NSA Cyber @NSACyber
159K Followers 12 Following We protect our nation’s most sensitive systems against cyber threats. Likes, retweets, and follows ≠ endorsement.

Zack Korman @ZackKorman
17K Followers 2K Following Cofounder @ Embroidery. Building AI cybersecurity stuff.
SolidSnake @soolidsnakee
1K Followers 357 Following Senior Malware researcher at @Elastic. Private account. All opinions expressed here are mine only (not of my employer etc).
Wraithwatch @wraithwatch
684 Followers 0 Following Wraithwatch is building the perception and control layer for next generation, mission critical AI.
Codex Changelog @Codex_Changelog
30K Followers 1 Following Unofficial Changelog for OpenAI's Codex CLI
Theo - t3.gg @theo
390K Followers 4K Following Full time CEO @t3dotcodes & @t3dotchat. Part time YouTuber, investor, and developer
Jamf Threat Labs @JamfThreatLabs
362 Followers 35 Following Mac security research and threat hunting team. Sharing findings discovered by @JamfThreatLabs at @JamfSoftware.
Firecrawl @firecrawl
86K Followers 4 Following The web data API to search, scrape, and interact at scale. 🔥
JFrog Security @JFrogSecurity
6K Followers 309 Following The JFrog Security Research Team empowers developers and companies to excel by identifying, prioritizing, and mitigating software risks.

speedrun @speedrun
39K Followers 303 Following Create The Future | Apply to our startup program: https://t.co/CDm2GrEGXu
Laser Wars @laserwarsHQ
5K Followers 384 Following A newsletter about military laser weapons and other futuristic defense technology by @iamjaredbkeller
Sergey Levine @svlevine
137K Followers 144 Following Associate Professor at UC Berkeley Co-founder, Physical Intelligence
Axios @axios
858K Followers 1K Following Smart Brevity worthy of people's time, attention and trust. Subscribe to our newsletters: https://t.co/uMitaJIcpz

Gradient Robotics @gradientrobots
1K Followers 0 Following Intelligent autonomous robots for industry.Trends for United States
You might like