Aexyn @stHackPointer
Yet another Red Teamer Joined April 2017-
Tweets453
-
Followers158
-
Following289
-
Likes1K

Pen testers will soon lose their job

GPT-6 Astra test 4/n Prompt: "Implement pen spinning with a dexterous hand. Use Isaac Lab for RL training, use the Sharpa hand, and create the pen mesh yourself. Give me a trained RL policy and a visualization video. You are free to search the web and download papers or anything
🐐

« Il s'agit d'une “attaque plus sophistiquée que ce qu'on avait vu par le passé”. »
🔥 We “hired” Lazarus APT remote workers — and uncovered their toolkit. @BirminghamCyber & @north_scan used #ANYRUN Sandbox to capture weeks of Famous Chollima activity inside a fake startup. 👀 How not to let a spy in? See full story and videos: any.run/cybersecurity-…


Releasing DCOMIllusionist as part of our talk on DCOM at @x33fcon with @k3vinTell. It's a remote in memory fileless lateral movement technique based on some research of @tiraniddo github.com/synacktiv/DCOM…

THEY ARE GOING TO BAN VPNs THEY ARE GOING TO BAN VPNs THEY ARE GOING TO BAN VPNs THEY ARE GOING TO BAN VPNs THEY ARE GOING TO BAN VPNs THEY ARE GOING TO BAN VPNs THEY ARE GOING TO BAN VPNs THEY ARE GOING TO BAN VPNs THEY ARE GOING TO BAN VPNs THEY ARE GOING TO BAN VPNs
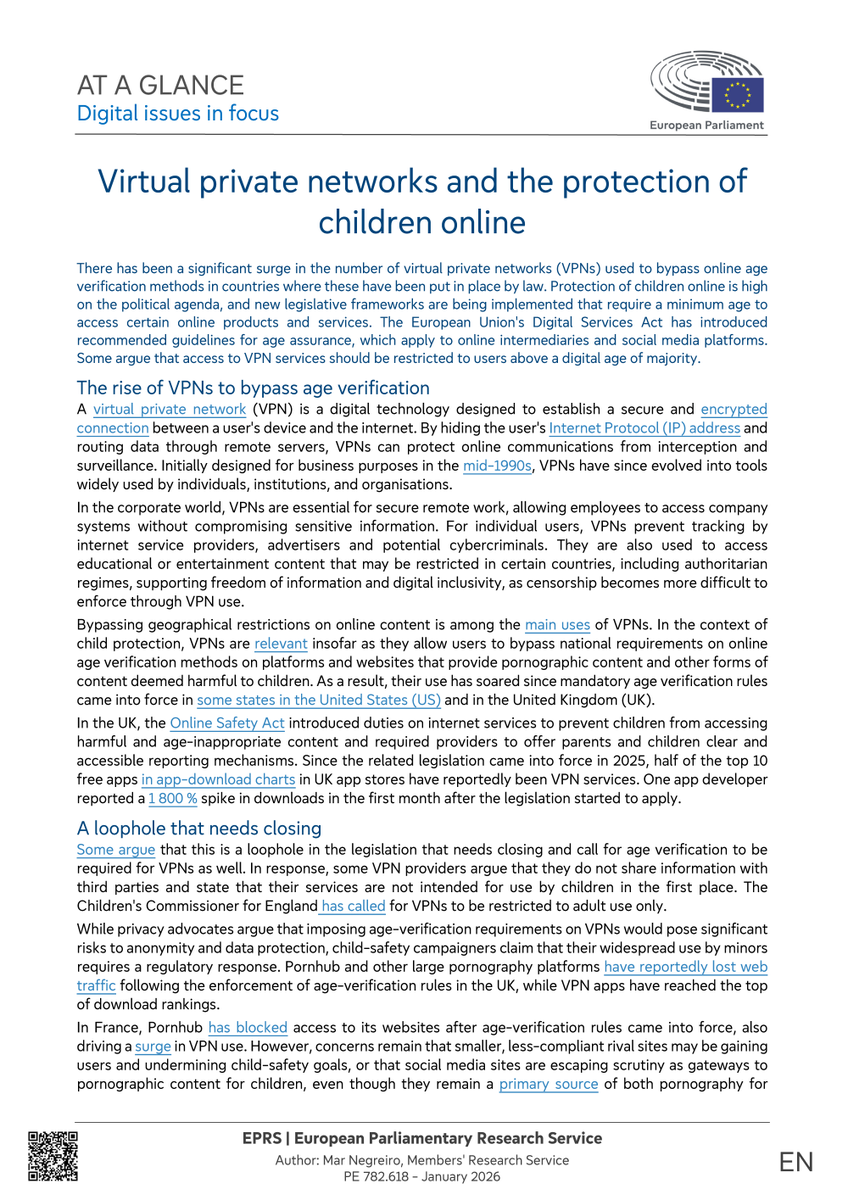
Virtual private networks #VPN are increasingly used to bypass online age verification. Protecting children online is a priority, with new rules being implemented requiring a minimum age for access to some services Read👉 link.europa.eu/FGfr6C #DSA @EP_Justice @FZarzalejos

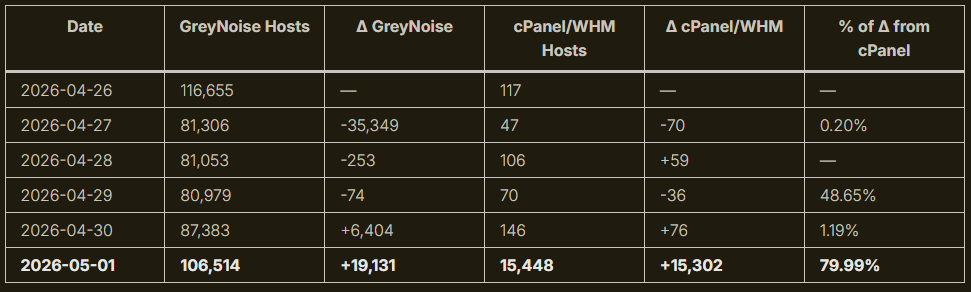
🚨 The cPanel Situation Is Spiraling Fast On April 29, CVE-2026-41940 was disclosed: a critical pre-authentication bypass in cPanel/WHM that lets remote attackers skip the login flow entirely and gain elevated access. Within 24 hours, it was already being weaponized. Censys watched the fallout in real time. The 6-day timeline (cPanel hosts flagged malicious): Apr 26: 117 Apr 27: 47 Apr 28: 106 Apr 29: 70 Apr 30: 146 May 1: 15,448 On May 1 alone, total malicious hosts jumped by +19,131, and 15,302 of those (roughly 80%) were cPanel/WHM systems. Compare that to the prior days where cPanel made up well under 1.2% of daily changes. This was not background noise. It was a coordinated spike. Top affected providers: DigitalOcean: 1,043 Contabo: 716 OVH: 501 Vultr: 391 Oracle: 321 Unified Layer: 280 Hetzner: 277 Akamai/Linode: 275 GoDaddy: 209 Microsoft: 169 With 1,052,657 cPanel/WHM hosts exposed on the public internet and only 9,595 currently flagged as malicious, the attack surface is enormous and growing. At least two campaigns are running in parallel: a Mirai botnet variant (nuclear.x86) deployed post-compromise, and a ransomware campaign tied to the Sorry/Hidden-Tear family. Ransomware footprint: ~7,000 cPanel servers with ".sorry" encrypted files 6,465 hosts: index.html.sorry 1,637 hosts: index.php.sorry 795 hosts: wp-config.php.sorry Victims directed to attackers via qTox If you run cPanel/WHM, patch immediately. Source: censys.com/blog/the-cpane…

Ce n’est pas une théorie. C’est déjà arrivé. En Utah. Étape 1 : loi de vérification d’âge contre les sites pornographiques. Étape 2 : la loi échoue. Les utilisateurs contournent avec des VPN. Étape 3 : nouvelle loi. Restriction d’usage des VPN. Pas limitée aux mineurs ni au porno. C’est exactement le pattern que je décrivais ce matin. → “Donnez-nous vos données pour votre sécurité” → La solution ne fonctionne pas → Les utilisateurs trouvent un contournement → On légifère contre le contournement Virkkunen disait le 29 avril que rendre l’app “non contournable” était “une partie importante des prochaines étapes”. L’Utah vient de nous montrer ce que ça veut dire concrètement.
The age verification law against porn in Utah failed. They created a new law blocking VPN use that is not being limited to youth and porn. pcmag.com/news/utahs-age… Exactly what every person concerned about privacy warned would happen...


💊 Emojis used as coded language to promote illegal activities online? Some platforms are now detecting emojis used as code for drug sales. This is one of the key findings of the first EU-wide report on systemic online risks. Dive in → link.europa.eu/CQhKGc #DSAForReal

The “age verification app” the EU wants to impose on the world got hacked in 2 minutes. Step 1: Present a “privacy-respecting” but hackable solution. Step 2: Get hacked (you are here). Step 3: Remove privacy to "fix" it. Result: a surveillance tool sold as “privacy-respecting”.
‼️🇪🇺 The EU's new Age Verification app was hacked with little to no effort. When you set it up, the app asks you to create a PIN. But that PIN isn't actually tied to the identity data it's supposed to protect. An attacker can delete a couple of entries from a file on the phone, restart the app, pick a new PIN, and the app happily hands over the original user's verified identity credentials as if nothing happened. It gets worse. The app's "too many attempts" lockout is just a counter in a text file. Reset it to 0 and keep guessing. The biometric check (face/fingerprint) is a simple on/off switch in the same file. Flip it to off and the app skips it entirely.


Next, Next, SYSTEM: Exploiting NSIS installer bugs to escalate privileges in Zscaler Client Connector In this blog post I show how patch gaps in Zscaler's bundled NSIS versions led to LPE.. includes PoCs and yara rule to help you find other affected s/w blog.amberwolf.com/blog/2026/apri…
Relayed NTLM creds are powerful, if you can use them. @senderend shows why browsers fail through ntlmrelayx SOCKS and introduces ghostsurf to make NTLM-authenticated web apps accessible. Read more ⤵️ ghst.ly/4tnJOtx

LOLEXFIL Living off the land Data Exfiltration method lolexfil.github.io
New @TrustedSec tool drop from @freefirex2 there is still gold to be fund in LNK files. github.com/trustedsec/Lnk…

Confirmation sérieuse : le ministère de l'Intérieur a bien été piraté. Ce ministère souhaite : - le scan des messageries (#ChatControl) - identification+preuve d'âge sur les réseaux sociaux "Aucune raison de craindre des fuites d'informations personnelles sensibles"...
Piratage du ministère de l'Intérieur: auprès de BFMTV, les équipes de Beauvau confirment que les hackers ont eu accès "à des applicatifs métiers". Autrement dit, des outils et logiciels internes, avec potentiellement à la clef des accès à des bases de données.
🔥Introducing a new Red Team tool - SessionHop: github.com/3lp4tr0n/Sessi… SessionHop utilizes the IHxHelpPaneServer COM object to hijack specified user sessions. This session hijacking technique is an alternative to remote process injection or dumping LSASS. Kudos to @tiraniddo for first discovering this years ago. Blue Team tip: Look for unusual child processes spawning from HelpPane.exe

My very first blog post is live: kiddo-pwn.github.io/blog/2025-11-3… During research, I've run into and documented a simple universal SQLite Injection RCE trick. Enjoy! N-day Analysis about Synology Beestation RCE (CVE-2024-50629~50631) by legendary DEVCORE 🎃 🍊 Thanks to @u1f383 @orange_8361 for original finding and allowing to post, and to @the_emmons for the invaluable references 🔥 Enjoy the Demo! PoC: github.com/kiddo-pwn/CVE-…

Cloudflare has recently started blocking proxy tools like Burp Suite by identifying their unique TLS and request fingerprints. If you encounter this issue, install the “Bypass Bot Detection” extension from the BApp Store. This extension spoofs Burp’s TLS fingerprint, making it appear like normal browser traffic and bypass it.

Credential Guard was supposed to end credential dumping. It didn't. @bytewreck just dropped a new blog post detailing techniques for extracting credentials on fully patched Windows 11 & Server 2025 with modern protections enabled. Read for more ⤵️ ghst.ly/4qtl2rm

Parses cached certificate templates from a Windows Registry file and displays them in the same style as Certipy does github.com/outflanknl/reg…


Lucub0x @Lucub0x
18 Followers 2K Following Dad | Husband | Ethical Hacking | “Time is what determines security. With enough time, nothing is unhackable”, Aniekee Tochukwu Ezekiel
clairey17 @dermatologebru
6 Followers 260 Following Flowers grow in my loneliness, dreams in sparkling silence ⭐
Emma @Emmaaqqm
0 Followers 32 Following
scriptjunkie (Matt) @scriptjunkie1
7K Followers 2K Following Documentation is lies. Source is an abstraction. Assembly is the truth. Also at https://t.co/VYFZ0HHnQn and nostr npub10mx0gx3r2lszrrut8kvr5mt2m8r9ffhn
Okafor Christian @OkaforChri1349
6 Followers 156 Following
Sm1th001 @sm1th001
124 Followers 1K Following 🏴☠️ Don't be evil. ▫️ Linux & Bsd ▪️ Arduino / Raspberry Pie Fan ▫️ Coding Python / C++ Baby ▪️ Cyberpunk Lover ▫️ Pentesting Addict
the dreamer @Silky55__
315 Followers 2K Following DevOps Engineer | PowerShell | Dotnet | RE beginner
Advik @Ad_vi_k
71 Followers 4K Following
Clément Notin @cnotin
6K Followers 993 Following 😈 Security researcher: Identity (#ActiveDirectory #EntraID) and Cloud 🎉 #CTF @tipi_hack 👨💼 Works @TenableSecurity, but opinions my own
0xblank @0xblank
51 Followers 1K Following
sexy boy @sexyboy1736053
5 Followers 218 Following

Thomas Sankara @Fuesh
80 Followers 501 Following Guard your integrity & character with your life. Its the only thing that will be left of you when all the material things are gone.
pruno @pruno9
97 Followers 512 Following Your average Red Teamer. Also a gamer and cats lover (maybe too much).
Connor Johnson @CJ_Fortra
41 Followers 191 Following Lead Account Executive - Fortra's Offensive Security | @fortraofficial - Representing Core Impact, Cobalt Strike, Outflank Security Tooling (OST).

Helfer @realHelfer
4 Followers 58 Following
Barbara Viersen @BViersen
95 Followers 2K Following
m4 @m4strcpy
0 Followers 194 Following

leco @_lec0_
53 Followers 293 Following@InamKha88764530
25 Followers 249 Following @InamKha88764530 is temporarily unavailable because it violates the X Hateful Profile policy.
rosen @pierrosen
374 Followers 680 Following Red Teamer & Senior Cybersecurity consultant @WavestoneFR YoloSw4g CTF team member 😎
IvreSec @ivresec
506 Followers 502 Following Bienvenue sur IvreSec, le Twitter de l'InfoSec Ivre - Fanclub de @pentesteur #infosec #charlatans #parodyaccount À propos du compte : https://t.co/IzYM2OSZOv
somewhere @S0m3wh3r3_0
236 Followers 5K Following
Rauxam @Rauxam_
17 Followers 74 Following
R. @Romain_SEVERIN
68 Followers 225 Following
Agent Shiba 🕵️ @agent_shiba
483 Followers 2K Following FR 🇫🇷/EN 🇬🇧 I post/repost things I find interesting on geopolitics 🌐 , intel 📡, Shakhtar ⚒️ & Ukrainian football ⚽️
NOODLE @bragames2
434 Followers 857 Following I like to learn about Windows/Active Directory pentesting, Red Team stuff & Maldev enjoyer
World Wide Greg @MorelGrgory1
16 Followers 133 Following

Roni Bachar @Roni_Bachar
208 Followers 704 Following
She's a runner, she's... @xo_kinsley
66 Followers 615 Following #skater, #snorkeling, #hacker. Repaired computers for @DHSgov personnel. #OpenSource enthusiast. GA resident. Ex @USArmy. Supporter of human & animal rights.
leseminariste @le_seminariste
31 Followers 1K Following

Zephyr @ZephyrZ_FR
3 Followers 220 Following


3ldidi @3ldidi
10 Followers 649 Following
MH @JustMissingLeg
663 Followers 4K Following baby reverser, @bleizack, @securinsa, student @ ESNA • CTF @ret2school_fr • @infosec.exchange

bouchra @emily19krystal
9 Followers 252 Following

7 chakras @LesaffreLouis62
8 Followers 112 Following https://t.co/MPhvRv1M0r | https://t.co/wT6GIvaim2
FrenchBreaches @Frenchbreaches
19K Followers 2 Following Votre référence n°1 sur les fuites de données françaises
OrangeCon @OrangeCon_nl
1K Followers 218 Following The Dutch Cybersecurity Conference! Experience the Hackers Community in Amsterdam, on June 4th 2026!
DirectoryRanger @DirectoryRanger
37K Followers 108 Following This account assembles and disseminates information related to Active Directory and Windows security.
Fortra @fortraofficial
3K Followers 1K Following Fortra delivers AI-amplified data security software solutions that help organizations use and protect their data with confidence.
CERT Orange Cyberdefe... @CERTCyberdef
10K Followers 433 Following First Private CERT in Europe. Tweets are about vulnerability and cyber threats. Corporate account: @OrangeCyberDef / @OrangeCyberFR GPG KeyID: 0xBD54B276
Vlad Rico @RicoVlad
61 Followers 138 Following Pentester and UNIX guy // PGP=0x11dc6625d03ded38 // Trying to tweet only useful infosec related things
Olaf Hartong @olafhartong
18K Followers 981 Following @FalconForceTeam | researcher with a camera | Microsoft MVP | Snow man role model
CovertAccessTeam @Covert_Access
89 Followers 51 Following
Haifei Li @HaifeiLi
9K Followers 151 Following For contact in the security community. NOTE: All the tweets are totally my personal opinions, not about any of my current employer stuff.
Michael Bargury @mbrg0
9K Followers 576 Following Breaking agents. Building @zenitysec. BlackHat / OWASP ASI review board.
bearstech @bearstech
19K Followers 3K Following #SCOP d'experts du #LogicielLibre Confiez nous la performance de vos applications (hébergement, infogérance, #devops, #SRE, sécurité, efficacité énergétique)
/ˈziːf-kɒn/ @x33fcon
7K Followers 1 Following When Red meets Blue... The very first security conference for Purple Teams on the planet
Emeric Nasi @EmericNasi
5K Followers 422 Following CyberSecurity researcher and founder of BallisKit. I have a passion for all infosec subjects especially redteam and writing offensive tools!
Justin Elze @HackingLZ
74K Followers 5K Following CTO @TrustedSec | Former Optiv/SecureWorks/Accuvant Labs/Redspin | Race cars

Nathan McNulty @NathanMcNulty
19K Followers 1K Following Loves Jesus, loves others | Husband, father of 4, security solutions architect, love to learn and teach | Microsoft MVP | @TribeOfHackers | 🦋@nathanmcnulty.com
Md Ismail Šojal �... @0x0SojalSec
57K Followers 6K Following Cyber_Security_Re-searcher || Ai Re-searcher || AI-Sec|| Malware Analysis II iOS || Pwn || 0SINT || Project AI-StrikeSec || 0ldAccounts Suspended @0xSojalSec ||
mpgn @mpgn_x64
19K Followers 236 Following Flibustier du net ̿ ̿̿'̿'\̵͇̿̿\=(•̪●)=/̵͇̿̿/'̿̿ ̿ ̿ ̿ Podcast Hack'n Speak @hacknspeak / https://t.co/GyACSFg9mw
CCob🏴�... @_EthicalChaos_
10K Followers 435 Following Ceri Coburn: Hacker | R̷u̷n̷n̷e̷r̷ DIYer| Vizsla Fanboy and a Little Welsh Bull apparently 🏴 Author of poorly coded tools: https://t.co/P6tT2qQksC

ProjectDiscovery @pdiscoveryio
44K Followers 149 Following Real, exploitable vulnerabilities. No noise. Nuclei scans fast. Neo closes the loop. @pdnuclei × @neo_ai_engineer
Trackflaw @trackflaw
184 Followers 1 Following Trackflaw is a french startup specialized in offensive security and specifically in penetration testing.
Paul Seekamp @nullenc0de
18K Followers 637 Following I spend a significant amount of time reading security stuff. Co-Founder/Partner @CoastlineCyber https://t.co/ZQT5L8q2RO
Lee Chagolla-Christen... @tifkin_
14K Followers 828 Following I like making computers misbehave. Does stuff at https://t.co/YsrVyTjOY7. https://t.co/UsRIholZ3M

HackGit @hack_git
54K Followers 2 Following The channel was created for cybersecurity specialists 🥷 → Open Source Software → RedTeam → BugBounty → etc 🍻 https://t.co/0PYtBpfJ4f
Alice Climent @AliceCliment
3K Followers 279 Following Malware and EDR stuff @harfanglab 🤓 || PTC || Sister of @h313n_0f_t0r & @lauriewired
Octoberfest7 @Octoberfest73
9K Followers 194 Following Red Team | Offensive Tool Dev | 2x Course Author @ Zero-Point Security
Blue Team News @blueteamsec1
57K Followers 9K Following The cybersecurity home for the latest #BlueTeam, #DFIR, and #ThreatHunting news and tools.
Jon Gaines @GainSec
1K Followers 858 Following Head of Offensive Security @ Anduril; Adjunct Instructor at HCC by day. Hacker & Founder by night. 50 CVEs. Husband. Father. Skateboarder. Posts are my own.
DEFCON GROUP Paris @dcgparis
2K Followers 11 Following A reboot of the DEFCON GROUP Paris group. Free bimonthly meetups. If you would like to give a talk, contact us here: [email protected]
Andrew @4ndr3w6S
3K Followers 3K Following Detection Engineering @HuntressLabs | Prev. Practice Lead, TAC (Purple Team) @TrustedSec | @SpursOfficial Super Fan - COYS!
Nikhil Mittal @nikhil_mitt
21K Followers 438 Following Hacker, Infosec Researcher, Military Affairs & History, PowerShell, AD and Azure pwner, Creator of Nishang and others :) Founder @alteredsecurity
pruno @pruno9
97 Followers 512 Following Your average Red Teamer. Also a gamer and cats lover (maybe too much).
Oliver Lyak @ly4k_
9K Followers 268 Following Yet another security researcher 🔦 Github: https://t.co/7WFOFz17KI
mgeeky | Mariusz Bana... @mariuszbit
15K Followers 1K Following 🔴 Offensive Security Developer @ Outflank, Red Team operator, ex-AV dev, ex- malware researcher 🫖 Green tea lover
ekt0 @ektoplasma_
553 Followers 344 Following Malware analysis, RE, and DFIR Co-creator of DFIR-IRIS DFIR ninja @ Synacktiv
Will Dormann is on Ma... @wdormann
27K Followers 1K Following I play with vulnerabilities and exploits. I used to be here on Twitter but now I'm here: @[email protected] https://t.co/hXggdAVkSQ

Richard Ackroyd @rfackroyd
812 Followers 913 Following Cybersecurity engineer specialised in detecting threats and preventing attacks. Currently working as a staff in fintech/blockchain
Christopher Peacock @SecurePeacock
7K Followers 2K Following #PurpleTeam | Ex @RaytheonTech MSSP, @SCYTHE_IO, & @GD_OTS | Taught at BlackHat & DEFCON | #100DaysofSigma | Keep exploring, keep learning, and stay curious
Hakin9 @Hakin9
65K Followers 1K Following Hakin9 is a monthly magazine and online training provider dedicated to hacking and cybersecurity.
Justin Tunney @jartine
44K Followers 224 Following I built a C library that lets you compile 12kb static binaries that run natively on Linux, Mac, Windows, FreeBSD, OpenBSD, NetBSD and BIOS using just GCC/Clang.
n00py @n00py1
14K Followers 965 Following Retweeter of InfoSec/Offsec/Pentest/Red Team. Occasional blogger/Independent security research.
Adam Chester 🏴�... @_xpn_
40K Followers 555 Following TRACE at @SpecterOps | Blog at https://t.co/tjfTOllCEu
Zero-Point Security @_ZeroPointSec
14K Followers 6 Following
You might like