Chainloop @chainloop_dev
Governance infrastructure for the age of AI chainloop.dev Worldwide Joined May 2023-
Tweets56
-
Followers34
-
Following3
-
Likes18
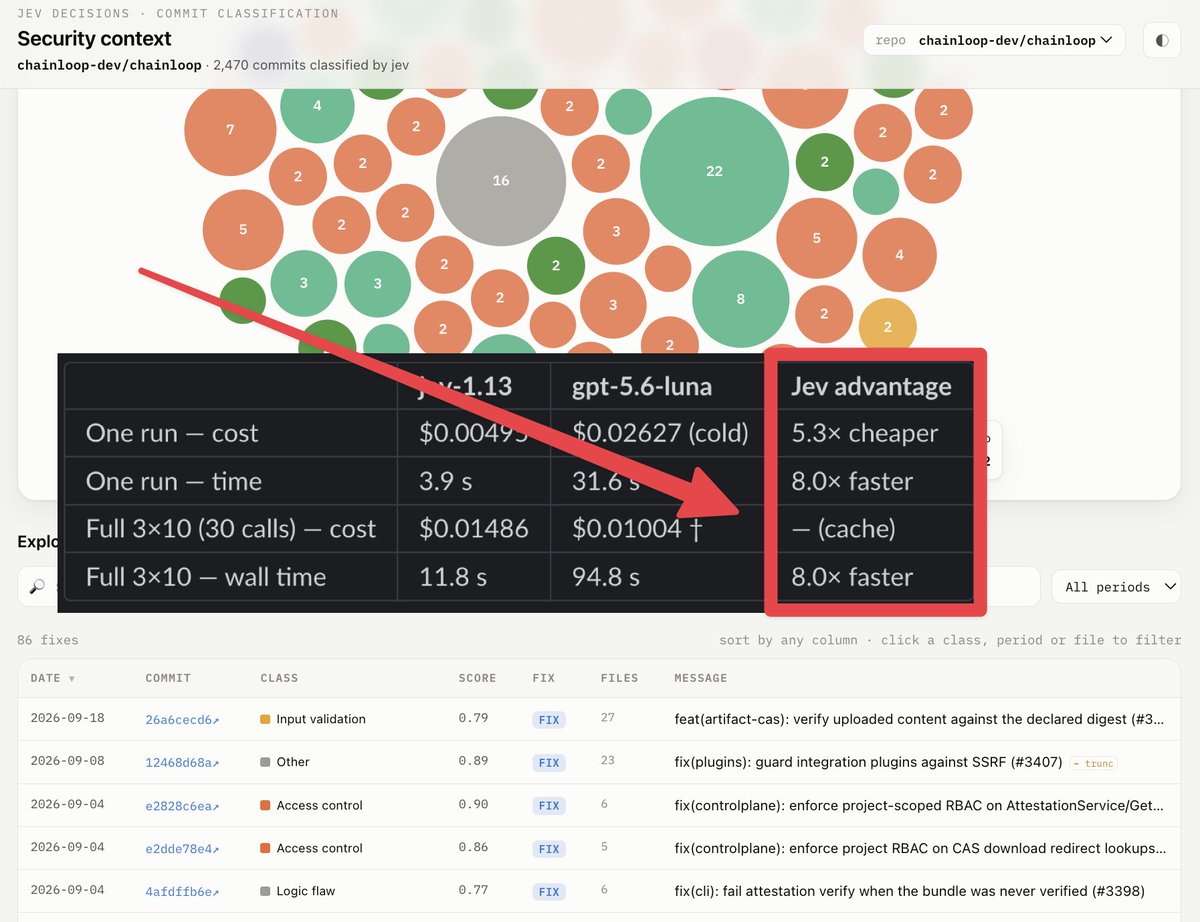
We are testing Jev from @typesafeai at @chainloop_dev for security classification, and the results are better than I expected. The task is simple to explain. Go through the full commit history of a repo and ask one question per commit: was this a security fix? Then classify the vulnerability and give a confidence score. This is how we build the AI Security Context for every connected repo at Chainloop. Why is this useful? (more in our docs, linked in the comments) 1. Find regressions and first-party vulnerabilities with adversarial analysis. Your AI agents get this context when they write code, so they know where the codebase got burned before and can hunt for unpatched variants of old bugs. 2. Measure the security hygiene of a project over time. Every confirmed fix is dated and classified, so you get an honest record: how fast you patch, how long bugs stayed exposed, which classes keep coming back. 3. Audit evidence. That record holds up in audits and security reviews, and it is a good way to judge a codebase before you depend on it. DM me if you want to try it. ps. Policies are next. Most of our agentic policies are the same problem anyway: here is the evidence, here is the question, give me a verdict with a reason and a score.
We ran this with great tools from our friends at @strix_ai and IronCurtain, on top of @AnthropicAI Claude Code, with proof-of-concept runs on @Kimi_Moonshot second opinions from @Zai_org GLM. @claudflare audit skill and @nvidia SkillSpector both earned their place.
We spent a month targetting AI security agents at our own code. We are a security company. Composition analysis, vulnerability scanning and secret detection already in CI. The agents found high-severity bugs anyway.
Methodology, tools, models, and what each one missed: chainloop.dev/blog/dogfoodin… We ran this with some great tools from our friends at
And one run is not enough. Our best single run found roughly half of what several runs found together. Fan out parallel hunters. Fan in adversarial validators.

A month of AI-driven audits against @chainloop_dev’s codebase found serious bugs that had passed review, tests, and CI. We fixed them and documented the experiment: bit.ly/3TcSEhh #AppSec #AISecurity
this is one of the reasons why cyber-security concerns around AI get it completely wrong human-slop code is full of so many security problems its mind blowing... most people have no idea just how bad it is the same LLMs that can be used to find them by bad guys can be used by vendors to patch them proactively and patch them before they're exploited
A month of AI-driven audits against @chainloop_dev’s codebase found serious bugs that had passed review, tests, and CI. We fixed them and documented the experiment: bit.ly/3TcSEhh #AppSec #AISecurity
Learn more and grab a slot: chainloop.dev/events/blackha…
Meet the Chainloop founders @danlishka & @migmartri at #BlackHat2026 Ask us for a demo! We will show you how we sandbox AI agents on-prem, govern AI coding sessions, and put vulnerability triage on autopilot: our AI agents assess the risk and open the fix PR, on your terms.

It works with Codex, Claude Code and Cursor, adding more soon!
If you are interested in what we are building re AI-Governance at Chainloop take a look at this article. AI adoption visibility through AI Coding Sessions and Session Alignment Scoring, enforcement through policies, compliance through controls. chainloop.dev/blog/ai-coding…
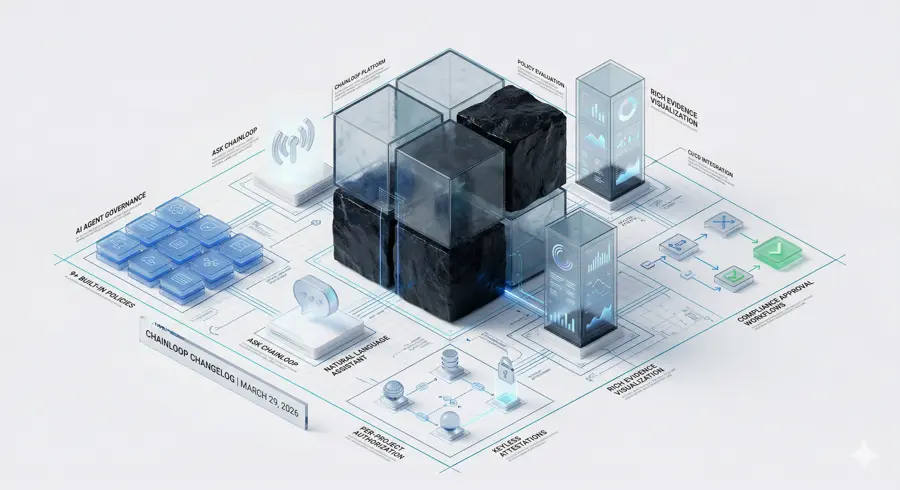
Changelog: AI Agent Governance, Ask Chainloop, and Supply Chain Hardening chainloop.dev/blog/changelog…
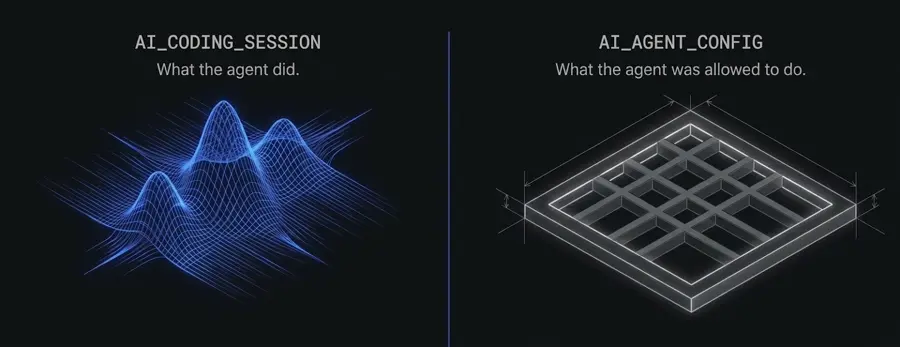
AI coding agents are writing your code. But who's governing them? We just shipped support for AI agent configuration and session evidence. Every instruction file, tool invocation, model used, every file changed, captured, signed, and policy-enforceable. chainloop.dev/blog/agentic-c…
Busy week for supply chain security. I know we're all busy building. But it's about time we stop for a moment and re-evaluate our security foundations. Supply chain security should be a first-class concern, not a post-mortem talking point. chainloop.dev/blog/litellm-s…
Last week Trivy got compromised. A security scanner, one of the most trusted in the ecosystem, quietly turned into a credential stealer. Pipelines kept running like nothing happened. We wrote about it. chainloop.dev/blog/trivy-sup…
Chainloop is joining @chainguard_dev Commercial Builds — hardened, zero CVEs, full provenance, FIPS-ready. Enterprises shouldn't have to choose between shipping software and trusting what's beneath it. chainloop.dev/blog/chainloop…
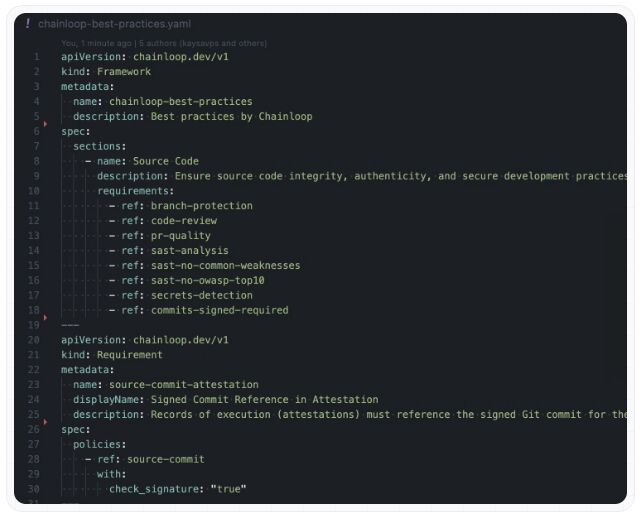
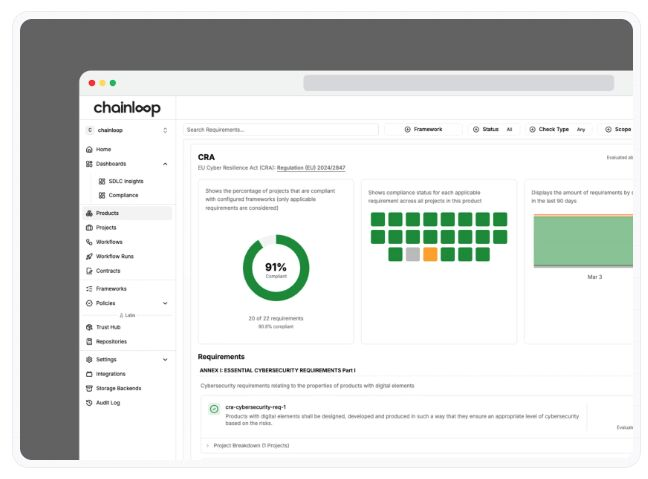
A new version of Chainloop just dropped With a new UI/UX foundation for what's to come, agentic policies and workflows support, new guardrails and security features, all of that is packed in this release. docs.chainloop.dev/changelog


Karolina Gronek @KaroChainloop
2 Followers 48 Following
Mateo Torres @torresmateo
763 Followers 1K Following Developer Advocate @tryArcade AAIF Ambassador · https://t.co/JpWPf2nk9c

XavSecOps @XavSecOps
1K Followers 3K Following DevOps, SecOps , AI Implementation AI is more than just intel, it's your new SysAdmin. Automating workflows, securing the stack, and redefining Red/Blue teaming
Eric Gallagher @ericgallagherwv
15 Followers 95 Following Author of "Securing the Backbone" newsletter | Helping organizations tame the complexity of open-source with @activestate 💪
Lily Mort @mort18613
2 Followers 86 Following

kumareshsomi @kumareshsomi
208 Followers 735 Following Dev | Engineering | Security | Netherlands | India. RT ≠ Endorsement.
Keyfactor @Keyfactor
2K Followers 1K Following Keyfactor is the identity-first security solution for modern enterprises.
julitrows @julitrows
346 Followers 95 Following 👨💻 Web Dev, Ruby on Rails specialist. 🎸 wannabe @carvingcolours. Opinions my own. he/him/his. 🐘: @[email protected] 🦋: https://t.co/BezGq6vCUD
Vuyo Soci @vuyo_soci
96 Followers 1K Following 4IR 🤗 ✌V.S Code. #systems #development #technology #ai #science #mathematics #innovation #process #data_science #programming #design #workflows

Flavio Granato @flaviogranato
0 Followers 222 Following
@[email protected] @fridex
213 Followers 674 Following Life is about priorities. @[email protected] 🐘
Tomasz Knura @tmk_knr
0 Followers 66 Following
Coldollar @coldollar
54 Followers 1K Following
OpenSSF @openssf
6K Followers 29 Following Open Source Security Foundation (OpenSSF) Together, we're securing the #opensource ecosystem #OSSSecurity https://t.co/uUpbn44G4Q https://t.co/adjLU8dbk0
Flanagrama @flanagrama
5K Followers 1K Following ¿Y hasta cuándo cree usted que podemos seguir en este ir y venir del carajo?
Christoph Raaflaub @chrira
179 Followers 382 Following
Mattia Buccarella @m_buccarella
78 Followers 47 Following
Rimas @Rimusz
2K Followers 2K Following @HelmPack co-founder. Senior DevOps @jfrog. Local & agentic AI. Every day is a gift from God — never waste it.
Javi Rodriguez @javirln
186 Followers 1K Following Founding Software Engineer at @chainloopHQ. @VMware / @bitnami @Travelperk @ClearPeaks alumni
Jesse Pickard @jessepickard
8K Followers 2K Following CEO of @themindcompany, makers of @elevateapp (Apple's App of the Year), @balanceapp (Google's App of the Year), and @playsparkapp (just launched!)
Fede Diaz @nordri
428 Followers 940 Following "As a platform engineer, I blend tech expertise with a love for hiking, homebrewing, and an ever-curious mindset. Let's explore together!"
Beltran Rueda @beltranrubo
741 Followers 924 Following Father of two and Sr Engineering Manager at Broadcom (previously Bitnami). Opinions are on my own.
Gonzalo Gómez Gracia @GonGomGra
223 Followers 478 Following Apasionado del baloncesto y enamorado de la niña más hermosa. Bitnami developer.
Miguel Ángel @miguelaeh_
155 Followers 302 Following I love the craft. Former founder at @pipeless_ai. Former @bitnami/@vmware engineer.
Cristian @cristiangauma
167 Followers 148 Following Paula’s husband and proud dad to Biel and Laia. Senior Manager Infrastructure & Software Engineering at https://t.co/DRqZ7DPPMY.
Santiago @torresariass
829 Followers 898 Following Assistant Professor of ECE and Security Bricoleur @PurdueEngineers | @arch_security | views are my own
John Kjell 🦉🛡�... @realjohnkjell
462 Followers 555 Following Open Source Leader @TestifySec - Securing software supply chains. Formerly - community college and Toys R Us “world leader”
Miguel Martinez Trivi... @migmartri
683 Followers 960 Following Giving your Software Supply Chain superpowers; co-founder at https://t.co/CDXbq5LdKu prev @bitnami, @vmware, Y Combinator Alumnus (W11)
Daniel Liszka @danlishka
199 Followers 591 Following co-founder & CEO @chainloop_dev | Helping ship trusted software | Previously @VMware & @Bitnami | Dad, biker, skier
dan ushman @danushman
24K Followers 4K Following Founder/CEO of @TrendSpider, @SignalStack & @SitDeck. Entrepreneur, trader & investor. I post about stocks, startups, tech, OSINT, ai, centrism & memes. Hi :)
Daniel Liszka @danlishka
199 Followers 591 Following co-founder & CEO @chainloop_dev | Helping ship trusted software | Previously @VMware & @Bitnami | Dad, biker, skier
You might like