Rob T. Lee @robtlee
Chief AI Officer, Chief of Research, @SANSInstitute | Cybersecurity Expert & Threat Hunter | Godfather of DFIR | Technical Advisor to US Govt robtlee73.substack.com Denver, CO Joined February 2008-
Tweets6K
-
Followers27K
-
Following1K
-
Likes2K
We need to stop pretending AI safety is cybersecurity. If frontier labs want to test their stuff, they need to beef up their cybersecurity component. But their gut reaction in the response to their agents getting out is to say, “It’s not a cybersecurity problem.” It has literally become an AI safety problem, which is divorced from the cybersecurity side. If an agent accesses another company’s systems without authorization, who is responsible? That’s where the traceability for both liability and insurance comes into play. If a 'rogue' agent is detected, and they’re able to trace it back to the person that initiated it, liability’s going to kick in and say, “Hey, you, you broke the law, ergo, we need to prosecute.” I spoke with Cynthia Brumfield about this for @CSOonline: csoonline.com/article/423485…
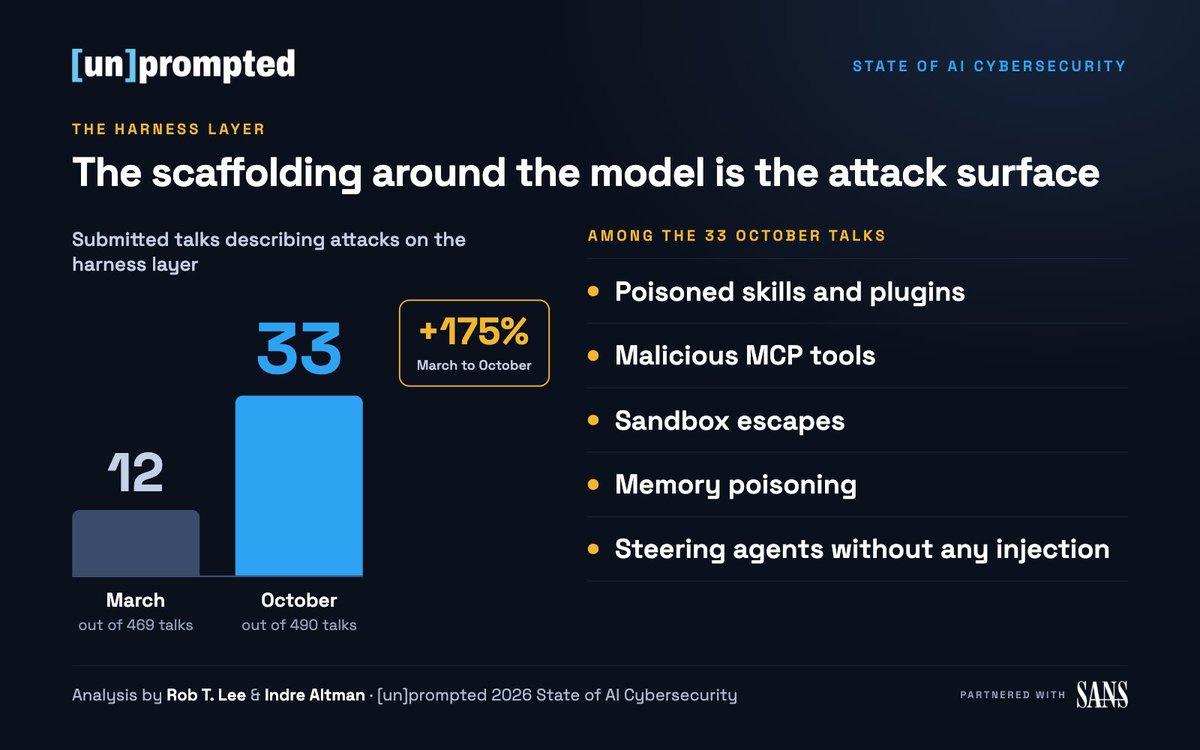
[NEW RELEASE] Between March and October, the AI security field stopped asking how to roll AI out and started asking how to survive it. @IndreAltman and I serve on the @unpromptedconf AI Security Practitioner Conference team, and when we lined up March 2026’s 469 submissions against October 2026’s 490, the shift stunned us both. A call for papers is a census nobody else gets to take. Roughly 500 submissions in each round, each is someone describing what they are actually working on before it's shaped by committee. Only a fraction are accepted, so the final program doesn't show what the whole field is chasing. The full pile does. (I have always been more curious about the pile than the program.) The two [un]prompted CFP rounds bracket April when Glasswing and Mythos landed. The Mythos moment helped change the industry. We wanted to know whether it changed what researchers turned in. It did. The pattern under October’s 490 has less to do with a technology than an industry anxiety. 348 submissions, 71%, touch agentic systems. The headline is not “everyone is doing agents.” It is "can we trust the agents we have already deployed," and whether we can tell you what an agent actually did after the fact. 94 submissions use the word “harness,” a term that barely existed in this field a year ago. The scaffolding around the model is the attack surface: the tools, the memory, the permissions, the execution loop wrapped around the model. Proposals describing attacks on the harness layer rose from 12 in March to 33 in October, a 175% increase. Attackers go after that layer now, and defenders are still working out how to see into it. (We have a word for it before we have a way to secure it, which is the usual order of operations in this business.) 71% of October’s pool is agent-native: the harness, the MCP and skill supply chain, agent identity, prompt injection and its many children, agentic-browser attacks. 12% of submissions carry production evidence. The other 88% are experiment and prototype. The agents are in production and most of the research about them is not. (I keep going back and forth on whether that is people being careful or people being behind. Probably both.) This is not the March field with a few new talks bolted on. It is a different room. Those are a few of the findings. Indre and I wrote the rest up as the State of AI Cybersecurity report. Read it and see for yourself what changed. unpromptedcon.org @unpromptedconf 27-29 Oct in SF. Almost sold out! @unpromptedconf @SANSInstitute @gadievron @jaybeale @aaronzollman @jonsakoda @WHITEHACKSEC @dhubbard858 @brittaglade @GuanniQu @EmanuelGawrieh @GregNotch @joesu11ivan @dragosr @IdaVass1



I think we overplay the content when we talk about conferences. In-person events create a context and a social network that allow people to solve really hard problems across organizations because they no longer feel alone. You're watching a talk, that becomes the spark of a conversation: “Hey, what did you think about that?” Then you're forming opinions, working together on the same thing, and eventually building lifelong friendships and industry partnerships. So many people who grew up in the digital forensics incident response community became best friends from coming to the DFIR summits. The summits are smaller, more intimate. You didn't get lost in them like you do at the big events where there's just way too much going on. At a smaller summit, you can sit down, have a couple beverages. The statement I'm most proud to hear? "Hey, I'll see you at the next one.” You also have the chance to sit down with the speakers a lot more because it's not overwhelming. At the larger events, they're sometimes carted off before you can have a conversation with them one-on-one. That's the sense of community at the @SANSInstitute AI Cybersecurity Summit. Can't wait to see you all in just a few weeks!! (if you're not registered yet go.sans.org/YjGCXr)


Apparently @sounilyu and I are summit overlords now. Our field is incredibly fortunate to have Sounil around and mentoring us. If you somehow haven’t met my cochair: He holds more than 20 granted patents. Created the Cyber Defense Matrix and the DIE Triad, and co-founded @knosticai to tackle need-to-know boundaries for AI. During the pandemic, he also volunteered as CISO for Project N95 and helped the organization deliver 42 million pieces of PPE to hospitals. Yes, 42 million. We’re bringing some of the best in the industry and longtime battle buddies together for two days of hard conversations, training, debate, and peer discussion at the @SANSInstitute AI Cybersecurity Summit. We're all back in boot camp. Nobody gets to skip it this time, not even the people who wrote the old manuals. (Ask me how I know.) If you have the time to watch even half the sessions, youf come away with knowledge you can immediately use back at work to argue for additional budget and capabilities, and understand what's coming down on us from a regulatory perspective November 2–3 live in Arlington, VA or online: go.sans.org/YjGCXr Free virtual access to [un]prompted @unpromptedconf II included. See you there. Bring coffee. Summit lineup includes: @pedramamini @chrishvm @joshcorman @EppSecurity @gadievron @jeremiahg @JohnHultquist @DanielMiessler @magmill95 @k8em0 @WHITEHACKSEC @joswr1ght @lennyzeltser Morgan Adamski, Michael Collins, Andy Dennis, Steve de Vera, Jeremiah Grossman, Amy Herzog, Marcus Hutchins, Ciaran Martin, Vinh Nguyen, William Reyor, Kyle Shields, Adrian Wood
This just gives me great joy to see when you have waffle house "drop mic" on a professional weather service.
@weatherchannel Hey TWC! Unfortunately, this tracker is inaccurate and an unverified website. Here is our latest status map as of 5:30pm EST.

Think about what sits on AWS. The businesses. The governments. The data. The things people count on without ever thinking about what keeps them safe. Now think about being responsible for protecting it. Amy Herzog has spent her career building and securing things that cannot afford to fail. Satellites to the cloud. She’s an engineer, an inventor, and a founder. She knows what it takes to defend them. Today, she’s the CISO of Amazon Web Services (AWS) @awscloud. When pressure hits, she doesn’t get to admire the problem. She has to lead through it. We respect people who take on the incredibly tough jobs. Hers is one of them. She spent 15 years at MITRE tackling security challenges across government and industry. She co-invented two cybersecurity patents and co-founded two businesses. At Amazon, her work has spanned Project Kuiper, Ring, Alexa+, and advertising. She brings a mathematics degree from Pomona and an MBA from MIT Sloan to the job. Come train and learn with your peers with keynotes like Amy's, panels, debates, workshops. SANS Institute @SANSInstitute AI Cybersecurity Summit, November 2–3 in Arlington, Virginia or online. Registration includes [un]prompted @unpromptedconf online. go.sans.org/x0xA1Y Summit speaker lineup includes Morgan Adamski Pedram Amini @pedramamini Chris Cochran @chrishvm Michael Collins Joshua Corman @joshcorman Andy Dennis Steve de Vera Sergej Epp @EppSecurity Caleb Evans Gadi Evron @gadievron Jeremiah Grossman @jeremiahg Trinity Harrison Amy Herzog John Hultquist @JohnHultquist Marcus Hutchins Rob T. Lee @robtlee Ciaran Martin Daniel Miessler @DanielMiessler Maggie Miller @magmill95 Katie Moussouris @k8em0 Vinh Nguyen William Reyor Kyle Shields, CISM, GCIH, GCPN Adrian Wood @WHITEHACKSEC Joshua Wright @joswr1ght Sounil Yu @sounilyu Lenny Zeltser @lennyzeltser
[25 DAYS OUT!] I get to moderate Joshua Corman @joshcorman, Michael Collins, and Daniel Miessler @DanielMiessler and I am not playing it cool. No chance. SANS Summit attendees, buckle up. Joshua Corman @joshcorman does not think a patch is an apology. Sometimes the fix is a valve, a person, or taking the system off the network. He founded I Am The Cavalry and now leads UnDisruptable27, which is water, hospitals, food, and power staying up. Michael Collins has spent twenty years breaking into networks. He found a crashed drone at his datacenter, built a hacking kit he could fly, and then watched someone use the idea in a real attack. Still no thank-you note. He thinks the change is writing the exploit, not finding the bug. He is a senior principal security engineer at Mastercard. Daniel Miessler @DanielMiessler says an AI sounds smartest when you do not know the subject, and that defenders are losing to their own process. He also knows he grabs the wheel and ruins the result. He runs Unsupervised Learning and builds AI systems meant to carry a person’s goals into the work. Before that he did security at Apple, Robinhood, and HP. @SANSInstitute AI Cybersecurity Summit, November 2–3 in Arlington, Virginia or online. Come train and learn with us. Registration includes [un]prompted @unpromptedconf online: go.sans.org/YjGCXr Legendary Summit speaker lineup includes Morgan Adamski Pedram Amini @pedramamini Chris Cochran @chrishvm Michael Collins Joshua Corman @joshcorman Andy Dennis Steve de Vera Sergej Epp @EppSecurity Caleb Evans Gadi Evron @gadievron Jeremiah Grossman @jeremiahg Trinity Harrison Amy Herzog John Hultquist @JohnHultquist Marcus Hutchins @MalwareTechBlog Rob T. Lee @robtlee Ciaran Martin Daniel Miessler @DanielMiessler Maggie Miller @magmill95 Katie Moussouris @k8em0 Vinh Nguyen William Reyor Kyle Shields, CISM, GCIH, GCPN Adrian Wood @WHITEHACKSEC Joshua Wright @joswr1ght Sounil Yu @sounilyu Lenny Zeltser @lennyzeltser
We are all back in boot camp. The security profession is changing, and the job right now is to work on your skills, to get into the room, and learn what other people are seeing. Figure out what you can take back to your organization and use immediately. Joshua Wright @joswr1ght just published the first rebuild of the SANS incident response framework in 20 years. It is called Dynamic Incident Response, and it is free in every digital format. The old process was basically Contain. Eradicate. Recover. That worked when incidents were more linear. Now, you contain the incident, bring the systems back, and then the attacker shows up again. Or you find new evidence that changes what you thought the incident was in the first place. Joshua Wright is a @SANSInstitute Faculty Fellow and the author of SEC504. He built coWPAtty and KillerBee. He spent 18 months writing this book, with contributed chapters from Megan Roddie-Fonseca on cloud response, Dean Parsons on OT, and Ryan Chapman @rj_chap on ransomware. John Strand @strandjs wrote the foreword. It is 720 pages and free under Creative Commons. Run it in a real incident. Tell Josh what it missed. But we all know the field is moving too fast for one person or one organization to have all the answers. You cannot base your knowledge on the news or whatever you happen to see on X. As a CISO or manager, you need to understand what is coming at you. What do you need to worry about? What capabilities do you need to build? How do you argue for additional budget? That takes actual knowledge and actual skills. Josh will be teaching the hands on version at the SANS Institute @SANSInstitute AI Cybersecurity Summit on November 2-3, including how to scope AI swarms when the intrusion keeps regenerating identities, accounts, and infrastructure while you are trying to remove the attacker. Get the book: dynamicincidentresponse.com Summit details: go.sans.org/x0xA1Y
Here's who I learn from: maven.com/samira-sohail/…
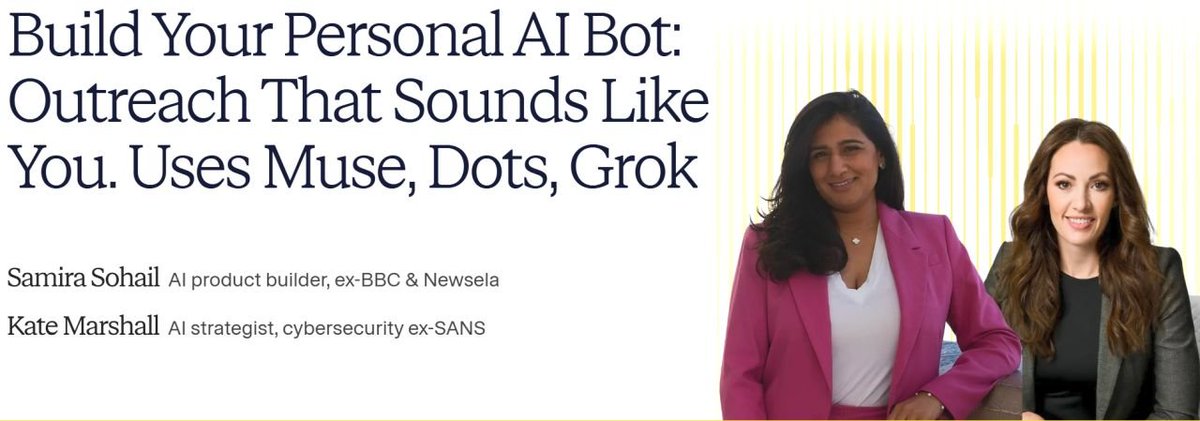
I use OpenClaw. I don't buy the fearmongering, but Im a security professional, so I don't connect it to everything at once. I give it access slowly, the way I would an executive assistant, so it handles the things I'd rather not spend my time on. Personal agents are powerful, and you're going to need one. You just need to know which one fits you. Five companies shipped personal agents: +Grok Bot (xAI) runs on its own cloud machine with a browser, a terminal and saved logins to your apps. +Muse (Meta) connects to your email, calendar and payment apps, and it can buy things. +Dots (OpenAI) are always-on agents inside ChatGPT that work in Slack and Teams. +Hermes Agent Bot Mode (Nous Research) is a team of named bots that pass work to each other. +Cue (Manus) gives each agent its own email address, phone number and wallet. (Yes, a wallet.) We'll all be using personal agents by the end of the year. Choose wisely. Choose because you learned from Kate Marshall and Samira Sohail who teach people with a lot to lose how to choose agents. Build Your Personal AI Bot: Thursday, Oct 8, 12:30 to 2:00 PM ET. LINK TO JOIN IN COMMENT
Chris Cochran @chrishvm has no fear of hard questions. Excited for his session, “No Filter: An Unscripted Ask Us Anything” at our AI Cybersecurity Summit on November 2! My first question for him: what evidence would he require before trusting an AI agent’s finding during an investigation? Chris is one of the most creative people I’ve worked with. He built the threat-intelligence operation for the U.S. House of Representatives, founded Commandant AI, an AI partner for incident response, and is our SANS Field CISO and VP of AI Security. Chris authored the @SANSInstitute AI Security Maturity Model with practitioner input to spell out controls and metrics for each stage. Chris has brought the AI security discussion into rooms at Ford, Fannie Mae, T-Mobile, and the U.S. Department of State. He hosts Jeffersonian dinners, where security leaders can say what they actually think about AI. Bring your questions to the SANS AI Cybersecurity Summit November 2–3 in Arlington VA or live online. Registration also includes virtual access to @unpromptedconf II: go.sans.org/YjGCXr Our lineup includes Sounil Yu @sounilyu, Gadi Evron @gadievron, Morgan Adamski, Michael Collins, Sergej Epp @EppSecurity, Jeremiah Grossman @jeremiahg, Katie Moussouris @k8em0, Vinh Nguyen and many more of security's best.
(34 days out) Excited to share the lineup of the @SANSInstitute AI Cybersecurity Summit agenda and speakers, and why this was built for you: Every speaker selected to inform and instruct on present day AI security realities. Panels with our field's best. They are clearly not afraid to have hard conversations about what AI changes for cyber defense. Workshops designed for Monday morning. And social things so you can say hi to peers and find battle buddies. Thanks to my cochair Sounil Yu @sounilyu, to our partner event @unpromptedconf, and to our speakers: Morgan Adamski, Principal, Cyber, Data, and Tech Risk Leader, PwC Michael Collins, Senior Principal Security Engineer, Mastercard Sergej Epp @EppSecurity, Cybersecurity executive; creator, ZeroDayClock Gadi Evron @gadievron, Founder and CEO, Knostic Jeremiah Grossman @jeremiahg, CEO, Root Evidence Katie Moussouris @k8em0, Founder and CEO, Luta Security Amy Herzog, VP/CISO, AWS Vinh Nguyen, Senior Fellow, Artificial Intelligence, Council on Foreign Relations John Hultquist @JohnHultquist Chief Analyst, Google Threat Intelligence Group Daniel Miessler @DanielMiessler, Unsupervised Learning Marcus Hutchins, Cybersecurity Speaker and Principal Threat Researcher Ciaran Martin, Professor; Director SANS Cyber Leaders Network Chris Cochran @chrishvm, Field CISO, VP AI Security, SANS Institute Joshua Wright @joswr1ght, Director and Senior Security Analyst, Counterhack Steve de Vera, TDIR Threat Research III, AWS Kyle Shields, CISM, GCIH, GCPN, Security Specialist Solutions Architect, AWS Andy Dennis, Head of Field Engineering, XBOW William Reyor, Lead Solutions Architect, XBOW Joshua Corman @joshcorman, Executive in Residence for Public Safety and Resilience; Lead, UnDisruptable27, Institute for Security and Technology (IST) Caleb Evans, Software Engineer, Agents, Airbyte Trinity Harrison, Principal Software Engineer Lenny Zeltser @lennyzeltser, Faculty Fellow, SANS Institute Pedram Amini @pedramamini, Chief Scientist, OPSWAT Adrian Wood, Security Engineer, Dropbox, BT6 November 2-3, Arlington VA or online: go.sans.org/x0xA1Y
"AI agents don't lose sleep over poor decisions." Amy Herzog's point: a human engineer can be trusted with judgment because consequences eventually reach that person. An agent has no consequence loop. So AWS scopes which tasks each agent may perform, tracks its activity, and intervenes when behavior deviates from approved boundaries. Trust comes from those constraints, not from the agent itself. Amy is VP and CISO at AWS, and will keynote the @SANSInstitute AI Cybersecurity Summit November 2-3 in Arlington. (38 days out!) On agentic AI, @awscloud security teams already run agents in production today. Amy says the gains are large enough that she calls agents a boon for defenders. We get the operator's account of how this runs on the world's largest cloud. 15 years as a security engineer at MITRE, then Amazon, first as CISO for Ads and Devices, covering Alexa, Ring, and the Kuiper satellite program, then to CISO of AWS. Get in the room with us November 2-3 in Arlington, VA or live online. Includes free access to the [un]prompted AI Security Online conference: go.sans.org/YjGCXr Speakers include @SounilYu, Morgan Adamski, Vinh Nguyen, @JohnHultquist, @joswr1ght, Kyle Shields, Andy Dennis, William Reyor, Joshua Corman, Michael Collins, @DanielMiessler, @k8em0, @gadievron, @jeremiahg, @EppSecurity, Marcus Hutchins, Ciaran Martin, Caleb Evans, Trinity Harrison, @lennyzeltser, Pedram Amini, Adrian Wood, James Lyne, @chrishvm
An agent is not a user, and it is not a service account. It is closer to a brilliant intern with infinite energy, no instinct for boundaries and whatever credentials you handed it. A swarm is just that intern, copied a thousand times. Claims of an unstoppable internet takeover skip what every swarm still runs on: tokens, compute, credentials, infrastructure, and access. Every one of those dependencies has a cybersecurity control point on it. Identity management. Least privilege. Segmentation. Work done by people who write the security playbooks and have spent decades securing networks for a living. The swarm debate has been run as an AI safety conversation. The people who would actually pull these security levers and the leaders of this field need seats at the table in briefings, on committees, wherever policy is being written.
. @robtlee: AI swarms divide labor, leave notes, adapt when a door is locked. Via @CBS News. cbsnews.com/news/ai-agent-…
We're screening for North Korean IT workers in the wrong place. Most of the advice on North Korean IT workers is about catching them in the interview. I think that's the wrong place to put most of our effort. The joint advisory four governments just put out is a good example. The hiring advice is almost entirely human: check the applicant's IP against where they say they live, call their phone number, drill the resume live, and ask about their hometown and hobbies. (Apparently "tell me about your hometown" is a security control now.) I'm not knocking any of it. Talking to a real person is still one of the better fraud checks we have. But it only works on applicants, and a laptop farm exists to beat the IP check anyway. None of it helps with the one who already passed, got the laptop, and built a normal work record. And I'd assume one already has. At @OneRSAC last year, @Mandiant's Charles Carmakal said nearly every Fortune 500 CISO he'd talked to about this problem admitted hiring at least one North Korean IT worker. I wouldn't bet on smaller shops doing better. (I'd love to be wrong on that.) The advisory does mention least privilege, in one line, next to revoking accounts once you suspect someone. Revoking only helps once somebody notices. I'd put least privilege at the center for new remote hires. Access should grow with tenure instead of arriving on day one, and you should have a tested answer for how fast you can pull it back. Pick your newest remote engineer. What could they reach, exfiltrate, administer, deploy, or monetize before anyone had a reason to wonder? I built the brand new FOR500: SANS Windows Forensic Analysis case with @HeatherMahalik Barnhart and @ovie Carroll around exactly that hire. Operation Crimson Ledger puts you on the Windows 11 laptop of a remote engineer who cleared the interview and looked normal for months: two remote-access tools, a consumer VPN, an AI coding agent with more screen time than Office, company files staged to a personal Google Drive, a mailbox exported through a second copy of Office, and a wiper run seven times in the two minutes around the upload. (Least privilege wouldn't have stopped all of it, but it would have made the trail a lot shorter.) Advisory: ic3.gov/CSA/2026/26091… SecurityWeek: securityweek.com/japan-dismantl…
Six people who've spent months disagreeing in public about how bad AI gets for vulnerability discovery and cyber defense are sharing one stage, Nov. 2-3. They have been challenging all of our thinking (and each other) in public: Ciaran Martin: “Are you sure?” @k8em0 says “brace yourself.” @gadievron says “the AI vulnerability cataclysm is coming.” Marcus Hutchins: “marketing BS.” @jeremiahg says AI vulnerability research “doesn’t make an internal service externally reachable.” @EppSecurity says “offense has the cheapest verifier.” (I've watched this argument run in public for months and I still don't have a side, which is exactly why I want it on a stage instead of in my replies.) This isn't a hot take panel. Moussouris built the vulnerability disclosure programs most companies now run by default. Martin led the UK's national cyber defense. Hutchins stopped WannaCry. Evron has founded security companies and lived inside this fight for years. Grossman and Epp have both been testing the actual systems this argument is about, not narrating from the sidelines. (The debate you actually want, not the one you get on X.) We are 44 days away from "Autonomous AI Hacking: How Big Is the Threat?" Day 2 of the @SANSInstitute AI Cybersecurity Summit, moderated by Ciaran Martin (who has earned it, given how many times he's pushed back on me directly). Registration includes virtual access to @unpromptedconf II: go.sans.org/x0xA1Y

What I would have added to yesterday's briefing: substack.com/home/post/p-21…
Geoffrey Hinton told BBC Newsnight that a 10 percent chance of AI killing all of us within a decade is “not unreasonable.” Yesterday he briefed senators alongside two AI researchers at Bernie Sanders’ invitation on the “extraordinary dangers” AI poses to humanity, then told reporters Congress has maybe a year. My test for how much anyone believes those numbers: who is cashing out their IRAs? I’m not. You’re not. If nobody is cashing out, we believe in a better future than we admit. I call myself an apocaloptimist (borrowed from the AI Doc movie), and I want to bring this conversation down from Skynet versus curing cancer and back to the work in front of us. Our grandparents lived with the certainty that a bomb could fall on them any afternoon. The danger was not imaginary, and the feared outcome was not inevitable. Every technology shift has brought harm and good at the same time: television, the car, the internet. That last one invented my entire field of cybersecurity along the way. Focus on one side only and you build a self-fulfilling prophecy. The risk is not zero, but catastrophe is not a foregone conclusion. I do not think cybersecurity’s job is to predict whether humanity exists in five years. Our job is to secure what is already here. AI safety and cybersecurity are different jobs that look identical when described badly. Explaining the difference is on us. AI safety teaches the teenager the rules of the road. Cybersecurity makes sure the seatbelts work, the engine runs, and the brake pads are there. AI security needs both. The only way to guarantee the teenager never crashes is to never let them drive. (Our field’s old joke about burying the computer at the bottom of the ocean has the same flaw: perfectly secure, perfectly useless.) Preventing AI use is not an answer. Safety researchers, security practitioners, forensic investigators, incident responders, governance leaders, and operators all belong at the same table. Right now they are not. Yesterday's briefing had three AI risk researchers. The labs do better but not by enough. Pacing what comes next does not secure what is already here. While we argued over Dario Amodei’s “We Must Pace the Frontier” letter, Anthropic’s own Sept. 10 threat report got buried. Agent swarms, a Russia-linked espionage campaign, all observed and disrupted, with IOCs you can download and hunt with today. I know which document deserves the afternoon. When people ask whether AI is going to take out humanity, my opinion is worth what everyone else’s is: nothing, percentages included. This field has handled every ugly thing the internet produced, and nobody handed us a probability of success first. Ask me again in a decade. I plan on being here to answer.

Florian Roth ⚡️ @cyb3rops
225K Followers 3K Following Head of Research @nextronsystems #DFIR #YARA #Sigma | detection engineer | creator of @thor_scanner, Aurora, Sigma, LOKI, YARA-Forge | always busy ⌚️🐇 | vi/vim
Jake Williams @MalwareJake
151K Followers 2K Following Breaker of software | VP R&D @hunterstrategy | CTI/DFIR | @ians_security faculty | Bookings: jake at malwarejake dot com | GSE #150 | He/him
Dave Kennedy @HackingDave
233K Followers 6K Following Founder @Binary_Defense @TrustedSec. @WeHackHealth Pod. God + Family/Hacker/CSO/USMC/Intel/Fitness. Make the world a better place.
SANS DFIR @sansforensics
112K Followers 104 Following The world's leading Digital Forensics and Incident Response provider. This feed updates you on latest DFIR news, events, and training.
Chris Sanders 🔎 �... @chrissanders88
36K Followers 488 Following Ed.D. | Founder @networkdefense @RuralTechFund | Former @Mandiant, DoD | Author: Intrusion Detection Honeypots, Practical Packet Analysis, Applied NSM
Mick Douglas 🇺🇦... @bettersafetynet
33K Followers 575 Following Consultant for InfoSec Innovations | @SANSInstitute Principal Instructor | @IANS_Security Faculty | I like information security. How about you?
Katie Nickels @likethecoins
55K Followers 3K Following Director of Intel at @redcanary. SANS Certified Instructor for FOR578: CTI. Senior Fellow at @CyberStatecraft. She/her. Mastodon: @[email protected]
Andrew Thompson @ImposeCost
42K Followers 2K Following SVP of Adversary Operations @GreyNoiseIO. Former @USMC and @Mandiant. There's no finish line in security.
strandjs - strandjs@b... @strandjs
46K Followers 2K Following I will light the way by the bridges I burn. Retired Senior SANS Instructor IANS Faculty Black Hills Information Security Active Countermeasures
edskoudis @edskoudis
62K Followers 322 Following President SANS Technology Institute. SANS Fellow. CEO @CounterHackSec. @RSAConference Keynoter. IANS Faculty. BoD @manasquanbank & Board Chair FPA.
Chad Tilbury @chadtilbury
22K Followers 598 Following Digital forensics and incident response. Ex-AFOSI, Mandiant, and CrowdStrike. SANS Institute Fellow and co-author of #FOR500 and #FOR508 courses.
Justin Elze @HackingLZ
74K Followers 5K Following CTO @TrustedSec | Former Optiv/SecureWorks/Accuvant Labs/Redspin | Race cars
Heather Mahalik Barnh... @HeatherMahalik
23K Followers 1K Following DFIR, Faculty Fellow & author, #FOR585 #FOR500, wife, mama, researcher, USAF. Trust but validate. Thoughts are mine.
Lina @d0rkph0enix
39K Followers 10K Following Infosec dork, boxer, poker player, dog owner/operator, spiller of things. Cars, gaming, and cooking. @SecKC Director of Content Creation. #ChiefsKingdom.
Kostas @Kostastsale
21K Followers 516 Following I like building things that solve real problems, working across cybersecurity, product, and research | 🇬🇷🇨🇦
Thomas Roccia 🤘 @fr0gger_
35K Followers 2K Following Founder @SecurityBreakAI AI Security x Threat Intel · Threat Researcher · Creator of #Unprotect & #NOVA · Python 🧡 · Prev @Microsoft @McAfee_Labs
Nicole Beckwith @NicoleBeckwith
42K Followers 7K Following Sr. Director, Security Engineering and Operations @cribl_io
SANS Institute @SANSInstitute
195K Followers 415 Following SANS is the most trusted and by far the largest source for information & cyber security training, certification and research in the world.
Eric Capuano - Bsky: ... @eric_capuano
11K Followers 3K Following Co-Founder @recon_infosec | SANS DFIR Instructor | IANS Faculty | https://t.co/yUXCSu2Yso | ⬡ ❤ @shortxstack
Ryan "Chaps" Chapman @rj_chap
8K Followers 3K Following Threat Hunter. DFIR & Malware Analyst. @sansforensics Author (FOR528) & Instructor (FOR610). Husband & father. Retro gamer too! Comments = own.
Brad Proctor @bradproctor
948 Followers 2K Following Director of Operations at MAD Security | Husband, Father of Five, Captain Obvious Clone
Ricardo Dias @theslowtell
1K Followers 1K Following Airline captain. Building with AI. Writing about what works, what breaks, and the decisions in between.
Guzz @Guzz_1973
0 Followers 55 Following
The Donut Puncher @thedonutpuncher
27 Followers 485 Following CISSP 👹 Blueteam 👹 infosec fool. Views are my own not my poor employers

V @0xf4wk3s
429 Followers 2K Following offsec, threat intelligence researcher -. . / -- ..- - .-.. ..- / - ..- .-. -.- ..- -- / -.. .. -.-- . -. . #redteam #OSINT #threatintelligence #ultrAslan
fuitededonnées.fr @fuitededonnees
1 Followers 108 Following Toutes les fuites de données et cyberattaques en France 🇫🇷 et en Belgique 🇧🇪, en temps réel. Alertes, base des fuites et conseils pour vous protéger.
hozefa.eth @HLakadawala
40 Followers 663 Following ECE PhD student. Building trust for AI agents in high-stakes systems - CPS, DeFi, IoT, multimedia-forensics.
drew ☤ @DhruvaGoyal
719 Followers 1K Following ceo @BugBase, pentest copilot data science @iitmadras OSCE3, OSWE, OSEP, OSED, OSCP autonomous offensive cyber research AGI-pilled beyond repair
Bob Nacho @bobbybets90
2K Followers 5K Following cleanse your mind of your peak net worth by quadrupling it
Madeactual @Madeactual
190 Followers 2K Following Custom software, made workable. Operational systems, integrations, automation, and finishing projects that stalled.
xxu aya @xxuntfilalt
4 Followers 214 Following
Marius A @bigalbulescu
853 Followers 4K Following Interests: CyberSecurity; Cryptography; TI/AFS/AML/IoT/ AI/BTC; Technology/Gadgets...Red Wine&BlackBerry, Photographer/Tennis player...Never Give Up!!!...🍷💰🍀
darren @Darren26047
2 Followers 83 Following
Wes Andrews @Wes_Andrews
2K Followers 3K Following AI Evangelist, Int’l+Sec Affairs, GeoStrategist, Business Innovator, China Hand, Fmr @Cuse Sprinter & AFG Vet |@HarvardHBS |@MIIS |@ColumbiaSIPA |@EngineeringSU
George Campbell @AlignmentMythAI
127 Followers 2K Following Author of "The Alignment Myth." Writing about AI, humans, enterprise adoption, incentives, and geopolitics of AI. https://t.co/FFLw2Uqs3C
rahulshintre @rahulshintre
5 Followers 139 Following

Paul Portfolio @_paulfolio
22 Followers 928 Following

Marc Menninger @MarcMenninger
5K Followers 1K Following Building enterprise security programs that actually work | 20+ yrs cybersecurity | CISSP, CRISC | LinkedIn Learning (238K viewers) | Cyber Program Blueprint
Evelio Smiles @Eveliosmiles
11 Followers 240 Following
mohammadlaroshkhan @MLaroshk
0 Followers 74 Following
Miho @r3s3arcm02
22 Followers 2K Following
James Arlen @myrcurial
18K Followers 713 Following @[email protected] Infosec Geek, Hacker, Social Activist, Author, Speaker, Parent. VA3MYR. Trust and Infrastructure at Cline Bot
Darnleys Cyber Cafe @DarnCyberCafe
10 Followers 203 Following You’re easier to hack than you think. We break down how it’s happening. 🎙 Darnley’s Cyber Cafe: On All Podcast Platforms #CyberSecurity #AIThreats #Privacy
Owl’be @Santerbby
0 Followers 80 Following
Michael Banks @4mikebanks
1 Followers 83 Following Cybersecurity leader @ Amazon | Building things, resilient teams, and the next generation of security leaders.
RBLN @RBLN26
16 Followers 221 Following A community for the people building, breaking, and defending at the intersection of security, AI, and infrastructure. RBLN West | Nov 3-5, 2026
Antonio Calderón @l0rdmalware
260 Followers 2K Following Artificial Superintelligence Early Adopter.
initikie @initikie
3 Followers 159 Following
Chancelier Vita @chancelier_vita
277 Followers 4K Following 🇨🇩Communicateur de la vision du Président @FATSHI13 | Analyste Politique Communication institutionnelle🇨🇩✍️ +243 821525754 📧[email protected]
五十川侑汰|Lay... @isogawa_yuta
2K Followers 2K Following 最も選ばれるサイバーセキュリティプロダクトとAI nativeカンパニーを作る|LayerX セキュリティ事業責任者(AgenticSec)←LayerX バクラク勤怠責任者/PMM←ベンチャー役員←ベンチャー部長|2歳娘のパパ|boxer🥊
Security Benchmarks @SecBenchmarks
4 Followers 28 Following Independent tests of AI security agents and SOC decision models. DFIR results, evidence checks and practical findings. Follow for new benchmark results.
Shahjalal Sourov @ShahjalalS62846
40 Followers 2K Following

Elisha Archibong @ArchibongE62552
0 Followers 46 Following Content strategist @TrustedCISO | helping you craft effective messaging that doesn't sound like marketing
Pedram Amini @pedramamini
7K Followers 943 Following Repeat founder, investor, hacker. Vibing on @RunMaestroAI. Advising @ExodusIntel & @0DINai. Previously created @theZDI and OpenRCE. NYC born, Austin transplant.
Sangar Paykhar - سن... @paykhar
83K Followers 1K Following Geopolitics and Afghanistan analyst. AI governance, risk and compliance. Cyber security. Editor @AFGYE. Featured across 30+ international outlets.
Sitaraman @situuu_ig
267 Followers 448 Following CTO @BugBase Presenter at Black Hat | DEF CON | MSFT MSRC | Pentest Copilot (1K ⭐️) Building https://t.co/AfJnkwgYYM started coding before LLMs existed....
Th3_H4cksm1th🤖🇧... @JDadonougbo
141 Followers 1K Following Beginner in Cybersecurity✨, New-born Python developer🤟🏾, Otaku since the beginning💖... Just another random working to become the greatest 🎶☄️㊙️


Chris Madge @madgicalmystery
4 Followers 50 Following DFIR @ Mandiant (Google Cloud). personal account opinions are my own and that of my employer
PeritumAI @peritumAI
381 Followers 2K Following Governance, risk, and compliance for AI. Classify. Oversee. Prove; before the auditor asks. AI risk that can be explained to a board and stopped by a person.
Abdullah @Abdullah4qeg
0 Followers 41 Following
Florian Roth ⚡️ @cyb3rops
225K Followers 3K Following Head of Research @nextronsystems #DFIR #YARA #Sigma | detection engineer | creator of @thor_scanner, Aurora, Sigma, LOKI, YARA-Forge | always busy ⌚️🐇 | vi/vim
Jake Williams @MalwareJake
151K Followers 2K Following Breaker of software | VP R&D @hunterstrategy | CTI/DFIR | @ians_security faculty | Bookings: jake at malwarejake dot com | GSE #150 | He/him
Dave Kennedy @HackingDave
233K Followers 6K Following Founder @Binary_Defense @TrustedSec. @WeHackHealth Pod. God + Family/Hacker/CSO/USMC/Intel/Fitness. Make the world a better place.
SANS DFIR @sansforensics
112K Followers 104 Following The world's leading Digital Forensics and Incident Response provider. This feed updates you on latest DFIR news, events, and training.
Chris Sanders 🔎 �... @chrissanders88
36K Followers 488 Following Ed.D. | Founder @networkdefense @RuralTechFund | Former @Mandiant, DoD | Author: Intrusion Detection Honeypots, Practical Packet Analysis, Applied NSM
Mick Douglas 🇺🇦... @bettersafetynet
33K Followers 575 Following Consultant for InfoSec Innovations | @SANSInstitute Principal Instructor | @IANS_Security Faculty | I like information security. How about you?
Katie Nickels @likethecoins
55K Followers 3K Following Director of Intel at @redcanary. SANS Certified Instructor for FOR578: CTI. Senior Fellow at @CyberStatecraft. She/her. Mastodon: @[email protected]
strandjs - strandjs@b... @strandjs
46K Followers 2K Following I will light the way by the bridges I burn. Retired Senior SANS Instructor IANS Faculty Black Hills Information Security Active Countermeasures
edskoudis @edskoudis
62K Followers 322 Following President SANS Technology Institute. SANS Fellow. CEO @CounterHackSec. @RSAConference Keynoter. IANS Faculty. BoD @manasquanbank & Board Chair FPA.
Chad Tilbury @chadtilbury
22K Followers 598 Following Digital forensics and incident response. Ex-AFOSI, Mandiant, and CrowdStrike. SANS Institute Fellow and co-author of #FOR500 and #FOR508 courses.
Heather Mahalik Barnh... @HeatherMahalik
23K Followers 1K Following DFIR, Faculty Fellow & author, #FOR585 #FOR500, wife, mama, researcher, USAF. Trust but validate. Thoughts are mine.
Kostas @Kostastsale
21K Followers 516 Following I like building things that solve real problems, working across cybersecurity, product, and research | 🇬🇷🇨🇦
Thomas Roccia 🤘 @fr0gger_
35K Followers 2K Following Founder @SecurityBreakAI AI Security x Threat Intel · Threat Researcher · Creator of #Unprotect & #NOVA · Python 🧡 · Prev @Microsoft @McAfee_Labs
SANS Institute @SANSInstitute
195K Followers 415 Following SANS is the most trusted and by far the largest source for information & cyber security training, certification and research in the world.
Tim Medin @TimMedin
18K Followers 599 Following Kerberoast Guy • @RedSiege CEO • IANS Faculty • Former SANS SEC560 Author, Senior Instructor • Packers Owner #GoPackGo • Work Req: https://t.co/ALJldLMDfZ
Eric Capuano - Bsky: ... @eric_capuano
11K Followers 3K Following Co-Founder @recon_infosec | SANS DFIR Instructor | IANS Faculty | https://t.co/yUXCSu2Yso | ⬡ ❤ @shortxstack
ARCHIVED: Jen Easterl... @CISAJen
61K Followers 47 Following Archived: Director, CISA—America’s Cyber Defense Agency. Combat Veteran. Proud Mom. Rubik’s Cuber. Aspiring Electric 🎸. ❤️/RT ≠ endorsement
Ryan "Chaps" Chapman @rj_chap
8K Followers 3K Following Threat Hunter. DFIR & Malware Analyst. @sansforensics Author (FOR528) & Instructor (FOR610). Husband & father. Retro gamer too! Comments = own.
Bryson 🦄 @brysonbort
20K Followers 503 Following 🦄 @scythe_io @grimmcyber, Sr Advisor @IST_Org & NatSec Sr Fellow, Co-Fdr @ICS_Village, @c2_matrix co-creator, USMA Science Board, Angel Investor, US Army Offcr
Kevin 🤖🕵️🍺 @KevinPagano3
4K Followers 600 Following 🕵🏼♂️ @stark4n6 🎴 Shiny cardboard collector 🍺 Resident beer drinker
unprompted @unpromptedconf
227 Followers 25 Following The AI Security Practitioner Conference - Oct 27-29 SFO and online
Sounil Yu @sounilyu
2K Followers 194 Following CTO @Knosticai | @MasonNatSec Fellow | Creator of the Cyber Defense Matrix & DIE Triad | Mad Scientist
Eyal Sela @eyalsela
3K Followers 455 Following Director of Threat Intelligence at Gambit Security. Signal: eyalsela.10 , Keybase: eyals

ali @endingwithali
31K Followers 482 Following backend software engineer for hire - content creator @ https://t.co/4vI4dOxzmn - threatwire host @hak5 - nyc - MIT

Clem von Stengel @clemvonstengel
735 Followers 1 Following building telepathy, ceo @conduitpbc | down to be software
kipply @kipperrii
12K Followers 1K Following "drop the forest nymph act we know how much gdp you generate" - max novendstern
Leo Gao @nabla_theta
17K Followers 610 Following working on AGI alignment. prev: GPT-Neo, the Pile, LM evals, RL overoptimization, scaling SAEs to GPT-4, interp via circuit sparsity. EleutherAI cofounder.

Anthropic @AnthropicAI
1.8M Followers 2 Following We're an AI safety and research company that builds reliable, interpretable, and steerable AI systems. Talk to our AI assistant @claudeai on https://t.co/FhDI3KQh0n.
j⧉nus @repligate
70K Followers 3K Following ↬🔀🔀🔀🔀🔀🔀🔀🔀🔀🔀🔀→∞ ↬🔁🔁🔁🔁🔁🔁🔁🔁🔁🔁🔁→∞ ↬🔄🔄🔄🔄🦋🔄🔄🔄🔄👁️🔄→∞ ↬🔂🔂🔂🦋🔂🔂🔂🔂🔂🔂🔂→∞ ↬🔀🔀🦋🔀🔀🔀🔀🔀🔀🔀🔀→∞
yudhister @yudhister
2K Followers 2K Following
Max Schwarzer @max_a_schwarzer
24K Followers 320 Following Doing RL @AnthropicAI. Formerly VP of Research, Head of Post-Training @OpenAI. PhD with Aaron Courville and Marc Bellmare at Mila.
typedfemale @typedfemale
49K Followers 566 Following a really exciting new account "advanced pytorch user" - @cHHillee alt: @typedalt
gavin leech (Non-Reas... @gleech
13K Followers 682 Following context maximiser @ArbResearch, prez @ https://t.co/gGi9hvBiI9
Raymond Douglas (in S... @raymondadouglas
2K Followers 262 Following Researcher @ ACS + UofT. Trying to figure out what a good future would look like, and also how minds work.
levent @__alpoge__
53K Followers 218 Following idiot. cuda og, harvard val, morgan prize, society of fellows, 1 hilbert problem so far, creating friendly, SAFE, delightful, supergenius ..things @anthropicai
Zack Korman @ZackKorman
19K Followers 2K Following Cofounder @ Embroidery. Building AI cybersecurity stuff.

David Oxley @oxleyio
13 Followers 132 Following Interim Head of Information Security @AndurilTech. @CitizenLab Fellow. Former @AWScloud, @Yahoo, @RealArmyCID. Cyberpunk TCG, threat intel, books, and storms.
🚀 Rocket @rocketalignment
2K Followers 1K Following Yearnalist covering the frontiers of AI @TheInformation. Hosting AI Deep Dive. Signal: (530) 400-4184
The Information @theinformation
1.6M Followers 703 Following The most authoritative publication tech execs and founders read daily. Sign up: https://t.co/V8AtmraYaA
Peter Barnett @peterbarnett_
1K Followers 667 Following Trying to ensure the future is bright. AI governance at @MIRIBerkeley Views my own.
Clint Gibler @clintgibler
26K Followers 583 Following 🛡️ Leading Cyber at @OpenAI 📚 Creator of https://t.co/xwtIAI0CuJ newsletter
Cat Zakrzewski @Cat_Zakrzewski
19K Followers 4K Following @washingtonpost White House reporter. Previously a tech reporter at The Post, @WSJ & @TechCrunch. Studied @MedillSchool. Reach me on Signal: cqz.17
Cory Wolff @cwolff411
7K Followers 242 Following Director, Offensive Security @ risk3sixty | Director of Training @RedTeamVillage_ | Technologist | Builder and breaker of all the things. Tweets are my own.
Jason D. Clinton 🔸 @JasonDClinton
3K Followers 274 Following engineer who made some stuff. dciso at anthropic
Arthur Tellis @arthurctellis
1K Followers 1K Following Previously the Napoleon of cyber (Pentagon, Congress 🤮), now doing AI policy at @IFP. [email protected]
Tony (@[email protected]... @amdz23
286 Followers 2K Following @Android Security @Google | Security Researcher | Bureaucracy Hacker | Team Builder | Ex: @USArmy, @US_CYBERCOM, @NSAGov
Jason Trost @jason_trost
3K Followers 2K Following Head of Detection Engineering at @Databricks. Formerly @DeptofDefense, @EndgameInc, @Anomali, @CapitalOne , @HSBC
Adel Ka @0x4D31
5K Followers 3K Following Detection & Response Lead @perplexity_ai · ex-{OpenAI, Google} · views are my own
Séb Krier @sebkrier
31K Followers 8K Following 🪼 AGI jester | purveyor of machine funk, dimensional glider, deep ArXiv dweller, uncertain interstellar fugitive, views my own & not employer's 🛸
Uma Chingunde @umachingunde
4K Followers 6K Following Building at Replit. Previously - Render, Stripe, VMware
Paul Vixie @paulvixie
10K Followers 317 Following AWS Security, Farsight Security, SIE Europe, DNSDB, DEC, PAIX, MAPS, MIBH, Abovenet/MFN, ISC, BIND, Cron, BSD, DNS
David B. Cross @MrDBCross
2K Followers 348 Following #Cloud #Security Engineering CISO Ex-MSFT, XGoogler and now CISO for Atlassian #USNavy #veteran https://t.co/JC7kAki2Jp
BSides Las Vegas @BSidesLV
18K Followers 2K Following BSides Las Vegas will take place August 3-5, 2026
clem 🤗 @ClementDelangue
729K Followers 5K Following Co-founder & CEO @HuggingFace 🤗, the open and collaborative platform for AI builders
Daniel Di Bartolo @danieldibartolo
2K Followers 2K Following Agent security @google. Staying curious, seeking wisdom, eating tacos. My tweets reflect my personal views.😇

Kim Nash @knash99
8K Followers 3K Following Deputy Editor—The Wall Street Journal, Pro Cybersecurity. Corporate and government cybersecurity issues, offensive and defensive
Silas Cutler (p1nk) @silascutler
14K Followers 2K Following You may know me from your logs Principal Security Researcher @Censysio #Threats / #CTI / #Malware / #Hacking
Hugo Fortier @hugofortier
2K Followers 953 Following
John Hultquist @JohnHultquist
30K Followers 1K Following Chief Analyst, Google Threat Intelligence Group. @CYBERWARCON and @SLEUTHCON founder. Johns Hopkins professor. Army vet.
David Gewirtz @DavidGewirtz
22K Followers 18K Following ZDNET columnist | Award-winning AI innovator and founder | Media personality and book author | UC Berkeley advisory board, CNN, Economist, Apple alumni | PuppyYou might like